
참고 자료 · 10
정보 무결성: 출처, 맥락 및 변환 검증
문서, 이미지 또는 비디오를 인용, 공유 또는 의사 결정에 사용하기 전에 검증하는 절차
업데이트됨 · 15 min

이 가이드가 달성하는 목표
- 가장 초기에 접근 가능한 버전을 찾습니다.
- 진짜 파일과 가짜 캡션을 구분합니다.
- 문서 변환 내역을 기록합니다.
- 흔적을 지우지 않고 수정합니다.
빠른 확인
- 누가 파일을 게시했고 어디에서 얻었습니까?
- 이전 버전이 존재합니까?
- 위치와 라이트가 호환됩니까?
- 메타데이터가 일관적이지만 충분한 정보로 간주되지 않습니까?
- 어떤 콘텐츠가 이 증거에 의존합니까?
단계별 방법
- 1
항목을 보존합니다.
URL, 접근 날짜, 수신 파일, 표시된 컨텍스트 및 법적으로 허용되는 경우 해시를 보존합니다. 사본을 사용하여 작업하고 모든 변환을 기록합니다.
결과물: 로그 항목 및 해시.
- 2
출처 추적
가장 초기 게시, 주장된 제작자, 중간 릴레이 및 잘리거나 재압축된 버전을 찾습니다.
결과물: 출처 체인.
- 3
내용 및 맥락 확인
지형, 건물, 날씨, 그림자, 언어, 연대기 및 알려진 사건을 비교합니다. 실제 이미지라도 장소나 날짜를 허위로 입력하면 재사용할 수 있습니다.
결과물: 확인 및 기각된 가설
- 4
메타데이터 검토
EXIF, 인코딩, 크기 및 이력을 단서로 활용합니다. 이러한 정보의 존재 여부만으로는 진위 여부를 입증할 수 없습니다.
결과물: 해석된 기술 기록
- 5
독립적인 검증
1차 자료, 다른 관점, 공식 기록 또는 독립적인 증인을 찾습니다. 동일한 파일에 의존하는 반복적인 내용을 식별합니다.
결과물: 확인 매트릭스.
- 6
게시 및 수정
신뢰도, 한계, 방법 및 출처를 명시합니다. 결론이 변경되면 연결된 페이지를 업데이트하고 날짜가 포함된 수정 기록을 유지합니다.
결과물: 편집 결정 및 수정 기록
이해하고 계산하고 판단하기
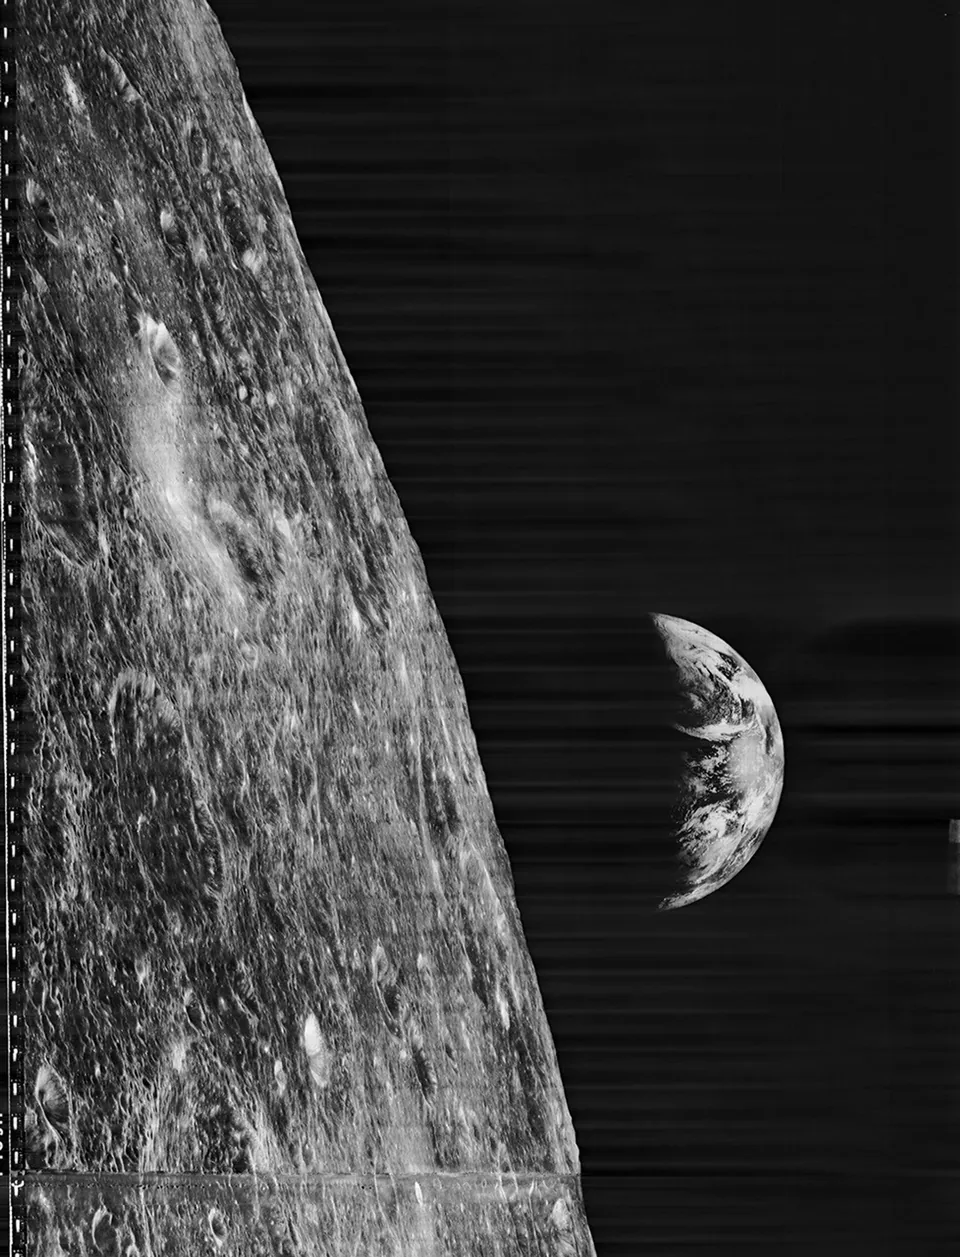
실제 사진: 파일, 설명, 페이지 날짜를 구분하기
이 Earthrise 이미지의 NASA 페이지는 Lunar Orbiter 1을 명시하고 NASA를 출처로 표시합니다. 페이지 날짜는 촬영일을 입증하지 않습니다. 제목만으로 탐사 임무를 특정할 수도 없습니다.
구체적인 주장을 정해 기관의 출처 페이지로 돌아가 확인하세요. 참조를 보존하고 표시를 위한 변경 사항을 기록합니다. 해시는 사본을 식별하지만 장면이나 해석의 진실성을 입증하지는 못합니다.
지표와 근거
| 지표 | 해석 | 필요한 근거 |
|---|---|---|
| 파일 | 검토한 사본 | 참조, 열람일, 해시 |
| 설명 | 출처가 공개한 귀속 정보 | 임무와 크레딧을 출처 페이지와 대조 |
| 권리 | 재사용 조건과 진위는 별개 | NASA 지침, 크레딧, 크기 변경 |
가상 예시
예시 상황
바이러스처럼 퍼진 이미지가 최근 사건을 보여준다고 주장합니다. 팀은 가장 오래된 게시본을 검색하고, 표시된 위치를 비교하고, 출처 메타데이터가 있는 경우 이를 확인합니다.
결정 및 예상 증거
메모에는 기술적 출처가 증명하는 내용, 독립적인 출처가 확인하는 내용, 그리고 아직 결론을 내릴 수 없는 내용을 구분하여 기록합니다.
관리 지표
| 지표 | 측정 대상 | 첫 번째 조치 |
|---|---|---|
| 출처 | 문서화된 출처와 연결된 항목 | 출처 없이 결정적인 증거 처리 |
| 입증 | 독립적인 단서로 뒷받침되는 결론 | 순환 반복 제거 |
| 수정 지연 | 오류 발견부터 콘텐츠 업데이트까지의 시간 | 종속 페이지 목록 유지 |
| 눈에 보이는 미지수 | 중요한 제한 사항을 명시적으로 기재 | 가설이 사실이 되는 것을 방지 |
일반적인 실수
- EXIF 정보 누락을 조작의 증거로 간주
- 역방향 검색 결과가 없는 경우 중단
- 재출판을 독립적인 출처로 간주
- 한 페이지만 수정하고 복사본은 수정하지 않음
자주 묻는 질문
메타데이터가 이미지의 진위 여부를 증명하는가?
아니요. 메타데이터는 제거, 변경되거나 장치에서 상속될 수 있습니다. 콘텐츠, 맥락 및 출처를 통해 이를 검증하십시오.
합성 콘텐츠는 어떻게 처리해야 합니까?
사용 가능한 출처 정보를 찾고, 일관성과 맥락을 검토한 다음, 관련 주장의 진위 여부를 평가하십시오.
오류를 삭제해야 합니까?
콘텐츠와 그 배포 방식을 명확하게 수정하십시오. 이미 독자에게 영향을 미친 경우, 조용히 삭제하는 것보다 날짜가 명시된 메모를 통해 변경 사항을 설명하는 것이 더 효과적입니다.
참고 자료: 데이터, 용도와 한계
문서 검토일 .
이 언어판의 상세 참고 설명은 영어로 제공됩니다.
| 출처와 목적 | 확인된 데이터 또는 기준 | 사용 방법 | 유지해야 할 한계 |
|---|---|---|---|
| FIRST · Traffic Light Protocol Indicate who may receive redistributed information. |
TLP 2.0 uses RED, AMBER, GREEN and CLEAR; AMBER+STRICT restricts sharing to the recipient organisation. Labels must not be translated. | Keep the marking with the information and check recipients before forwarding. Ask the source to clarify any ambiguity. | TLP is neither a formal classification nor a reuse licence. It does not guarantee content accuracy. |
| C2PA · Content Credentials Describe and verify certain content provenance information. |
C2PA specification 2.4 defines manifests, assertions and cryptographic binding mechanisms associated with media. | Examine what the manifest asserts, who signed it and whether validation succeeds. Test preservation after transformations and distribution. | Validated provenance does not establish the truth of a scene. Absence of a manifest does not demonstrate a fake. |
미디어 출처 및 C2PA 검증
이 언어판의 상세 참고 설명은 영어로 제공됩니다.
A provenance report combines findings with different scopes. Signature, credential trust, content binding and scene context are separate assurances. Retain the exact asset and full report before summarising a result.
References use C2PA 2.4, dated April 2026 in its version history. This explorer explains twelve selected codes; it validates no file, retrieves no manifest and detects no AI-generated image. Cases are fictional and proposed checks are editorial guidance.
References consulted on .
Read twelve C2PA codes without overinterpreting them
The groups below are those used by the specification: success, informational and failure. A success code describes its particular check rather than replacing full validation. Missing information and a failed check cannot be reduced to a fake label.
| Code and group in C2PA 2.4 | Reported finding | Proposed follow-up | Conclusion to avoid |
|---|---|---|---|
claimSignature.validatedSuccess · success | The claim signature validated. | Also inspect trust, validity period and binding to the relevant asset. | The whole scene is true or every validation check is complete. |
signingCredential.trustedSuccess · success | The validator recognises the signing credential as trusted. | Record the trust list, its version and applied policy. | A signer’s name alone confirms the depicted event. |
timeStamp.validatedSuccess · success | The time-stamp token passes the checks described in the specification. | Distinguish it from capture time and inspect trust in the time-stamping authority. | The attested time necessarily dates the photographed scene. |
assertion.dataHash.matchSuccess · success | The data-hash binding matches within the checked scope. | Inspect the assertion, excluded ranges and any other applicable bindings. | Every byte and every metadata field is covered without exception. |
signingCredential.ocsp.inaccessibleInformation · informational | An online OCSP check was attempted without a response. | Retain network conditions and distinguish no response from a returned status. | The certificate is revoked, or certainly not revoked. |
signingCredential.ocsp.unknownInformation · informational | The OCSP response reports unknown for the signing credential. | Read the report and the policy used to handle that status. | Unknown means good or revoked. |
ingredient.unknownProvenanceInformation · informational | The relevant ingredient has no C2PA manifest. | Identify that ingredient and what its history actually makes available. | All ingredients were verified or that ingredient must be fake. |
assertion.dataHash.additionalExclusionsPresentInformation · informational | The binding excludes ranges beyond the C2PA Manifest Store. | Identify the excluded regions and their relevance to the claim being examined. | A hash success automatically protects excluded metadata. |
claimSignature.mismatchFailure · failure | Claim signature verification fails. | Retain asset, manifest and report; compare with the available source copy. | The cause of failure or somebody’s intent is already established. |
signingCredential.untrustedFailure · failure | The credential appears on none of the validator’s applicable trust lists. | Check policy and lists; distinguish this from a mathematically incorrect signature. | The file must be fabricated or its signature must be mathematically invalid. |
assertion.dataHash.mismatchFailure · failure | An asset byte range does not match the hash declared in the assertion. | Identify the checked copy and its transformations before explaining the difference. | Every difference establishes intentional falsification of the scene. |
signingCredential.ocsp.revokedFailure · failure | The OCSP response indicates revocation under the applied check. | Read the temporal evidence and validation procedure behind the result. | A summary detached from its date and report establishes the status of every copy. |
No code matches the filters.
Four version details useful to editorial and technical teams
- Published version
- The examples above follow C2PA 2.4, published in April 2026. Version 2.5, published in October 2026, expands support for asset formats and live media. Record your validator version and check the status-code table for the corresponding edition before interpreting a result.
- specVersion
- In this version the recommended field belongs in claim_generator_info. It is informational; validators should not change logic solely because of its value.
- crJSON
- This JSON-LD representation is a derived view of C2PA data for reporting and interoperability. It is not independently verifiable or a validation input format.
- c2pa.ai-disclosure
- The assertion carries an AI transparency declaration. It is not a universal detector, and its absence does not prove human origin.
Six fictional situations for a publication decision
| Fictional situation | Concrete check | Decision proportionate to evidence |
|---|---|---|
| A signed photo receives a new caption | Match the asset and report against the scene, date and location claimed by the new caption. | Describe checked provenance and leave the event attribution unresolved if uncorroborated. |
| A resized variant no longer matches the old binding | Compare original, transformation tool, distributed variant and manifest associated with each. | Handle the validation break without inferring malicious manipulation from the hash code alone. |
| Two validators do not trust the same signer | Record versions, trust lists and policy, then compare other findings. | Explain the trust-policy difference rather than treating it as contradictory truths about the scene. |
| A screenshot no longer presents a Content Credential | Seek the earlier asset and document the known copy chain. | Retain the screenshot’s status and incomplete history; an absent manifest does not establish a fake. |
| A binding success accompanies excluded metadata | Identify excluded fields or ranges and caption claims depending on them. | Limit the conclusion to covered data and verify decisive fields another way. |
| A supplier sends only a crJSON report | Request the asset and provenance data needed for verification, plus tool version and policy. | Examine the report without claiming to have repeated cryptographic validation. |
Retain a usable verification record
- Exact object
- Examined asset or stream, known origin, copy and transformations.
- Tool and policy
- Validator, version, configuration and relevant trust lists.
- Complete findings
- Codes, relevant object, explanations and time evidence; keep inconclusive information as well.
- Examined claim
- Exact statement about location, date, creator or AI use and its source.
- Editorial decision
- What is established, what is missing and what could change the conclusion.
Examine information origins and repetitions →
Primary sources and limits of this reader
This is not an exhaustive C2PA code inventory. Full procedures, formats and trust policies remain those of the specification and your validator. Diagrams, cases and records are CIE teaching proposals.
- C2PA · Content Credentials Technical Specification 2.4 · 2.4 · April 2026 ·
§5.3.1; §14.3; §15.2; §15.7–15.12 - C2PA · Content Credentials Technical Specification 2.5 · 2.5 · October 2026 ·
Appendix D and Appendix F.1 - C2PA · Content Credentials Explainer · 2.4
§2; §7.2–7.4 - C2PA · Security Considerations · 2.4
§2.2–2.6; §4; §5
STIX 지표와 TLP 공유
이 언어판의 상세 참고 설명은 영어로 제공됩니다.
Check TLP scope before publishing an excerpt
A traceable note does not by itself grant permission to redistribute it. TLP markings, additional restrictions and intended recipients must accompany a redaction or publication decision.
- AMBER+STRICT limits sharing to the organisation; AMBER’s scope for protecting clients does not apply by default.
- GREEN excludes public channels; CLEAR does not remove copyright rules or separate restrictions.
- Check the marking of each quoted field and obtain explicit source permission if the intended sharing exceeds the received scope.
Read the STIX, observations and TLP sharing reference →
Sources checked on · FIRST · TLP 2.0
OSINT: 증거 보존
이 언어판의 상세 참고 설명은 영어로 제공됩니다.
Claimed provenance and preservation answer different questions
An edit history or manifest does not replace collection context. Preservation connects objects actually received, copies created and documented handling actions.
- Separate binary integrity, source identity and an assertion’s truthfulness.
- Keep derivative versions with their own identifiers and references.
- Document missing material before reaching a trust conclusion.
See copy lineage and the eight preservation cases →
Sources reviewed on · NIST · Digital Evidence Preservation · NIST IR 8387 · Full report · NIST · SP 800-86 · NIST SP 800-86 · Full report · NIST · FIPS 180-4 · Secure Hash Standard
PDF: 정보 삭제와 공유
이 언어판의 상세 참고 설명은 영어로 제공됩니다.
A documented transformation still needs release review
Derivative lineage explains technical provenance; it does not prove all excluded information was removed. Visible, hidden and embedded surfaces still need checking.
- Separate pending marks, applied redaction and hidden-data sanitization.
- Check a positive control before interpreting a negative search.
- Bind the decision to the delivered version and its recipients.
See surfaces and the pre-sharing review matrix →
Sources reviewed on · Adobe · Redacting and sanitizing PDFs · Adobe · Redact sensitive content · Adobe · Sanitize PDFs · ICO · Avoid accidental breaches when redacting · ICO · Hidden information in documents · Microsoft · Document Inspector
인용 사슬과 소셜 모니터링
이 언어판의 상세 참고 설명은 영어로 제공됩니다.
Separate origin, repost and corroboration
A capture or provenance signature may document a record without proving its claim. Before citing multiple publications, check whether they reference the same document.
- Keep the consulted version and its exact reference.
- Name missing citations instead of assuming their contents.
- Treat distinct documents as records to compare, without assuming independence.
Read the method and explore citation chains →
Government Communications · RESIST 3 · RESIST 3 · 2025 · consulted 2026-10-23
Government Communications · RESIST 3 quick reference · RESIST 3 · 2025 · consulted 2026-10-23
공식 참조
참조는 방법을 뒷받침합니다. 상황에 맞게 검사를 조정하십시오. 이는 인증이 아닙니다. 원본 참조 제목 및 소스 문서는 다른 언어로 작성되었을 수 있습니다.
참고 자료 확인일 .
- C2PA — Content Credentials Technical Specification 2.5
- UC Berkeley / OHCHR — Berkeley Protocol on Digital Open Source Investigations
- FIRST · Traffic Light Protocol
- C2PA · Content Credentials
- C2PA · Content Credentials Explainer
- C2PA · Security Considerations
- NIST · Digital Evidence Preservation
- NIST IR 8387 · Full report
- NIST · SP 800-86
- NIST SP 800-86 · Full report
- NIST · FIPS 180-4 · Secure Hash Standard
- Adobe · Redacting and sanitizing PDFs
- Adobe · Redact sensitive content
- Adobe · Sanitize PDFs
- ICO · Avoid accidental breaches when redacting
- ICO · Hidden information in documents
- Microsoft · Document Inspector
- Government Communications · RESIST 3
- Government Communications · RESIST 3 quick reference

