
Recursos · 10
Integridad de la información: verificar procedencia, contexto y transformaciones
Procedimiento para calificar un documento, imagen o vídeo antes de citarlo, compartirlo o utilizarlo en una decisión.
Actualizado · 8 min

Lo que esta guía ayuda a lograr
- Encuentra la versión más antigua accesible
- Separar un archivo genuino de un título falso
- Transformaciones de documentos
- Corregir sin borrar el rastro
Comprobación rápida
- ¿Quién publicó el archivo y de dónde lo consiguió?
- ¿Existe una versión anterior?
- ¿Son compatibles ubicación y luz?
- ¿Los metadatos son consistentes pero no se tratan como suficientes?
- ¿De qué contenidos depende esta evidencia?
Método paso a paso
- 1
Preservar el artículo
Conservar la URL, fecha de acceso, archivo recibido, contexto visible y un hash cuando sea legal. Trabaje en una copia y registre cada conversión.
Entregable: entrada de log y hash.
- 2
Traza procedencia
Busque la publicación más antigua, el creador reclamado, retransmisiones intermedias y cualquier versión recortada o recomprimida.
Entregable: cadena de procedencia.
- 3
Consultar contenido y contexto
Compara terreno, edificios, clima, sombras, idioma, cronología y eventos conocidos. Una imagen genuina se puede reutilizar con un lugar o fecha falsa.
Entregable: hipótesis confirmadas y rechazadas.
- 4
Inspeccionar metadatos
Utiliza EXIF, codificación, dimensiones e historial como pistas. Su presencia o ausencia nunca prueba por sí sola la autenticidad.
Entregable: ficha técnica interpretada.
- 5
Corroborar de forma independiente
Encuentra una fuente primaria, otro ángulo, registro oficial o testigo independiente. Identifique repeticiones que dependan todas del mismo archivo.
Entregable: matriz de corroboración.
- 6
Publicar y corregir
Estado de confianza, limitaciones, método y fuente. Si la conclusión cambia, actualice las páginas vinculadas y mantenga una nota de corrección fechada.
Entregable: decisión editorial y registro de correcciones.
Comprender, calcular y decidir
Fotografía real: distinguir archivo, leyenda y fecha de publicación
La ficha NASA de esta imagen «Earthrise» identifica Lunar Orbiter 1 y acredita a NASA. La fecha de la página no demuestra la fecha de captura. El título por sí solo tampoco identifica una misión.
Compruebe una afirmación concreta y vuelva a la ficha institucional. Conserve la referencia y anote cambios de presentación. Un hash identifica una copia, pero no demuestra que la escena o su interpretación sean verdaderas.
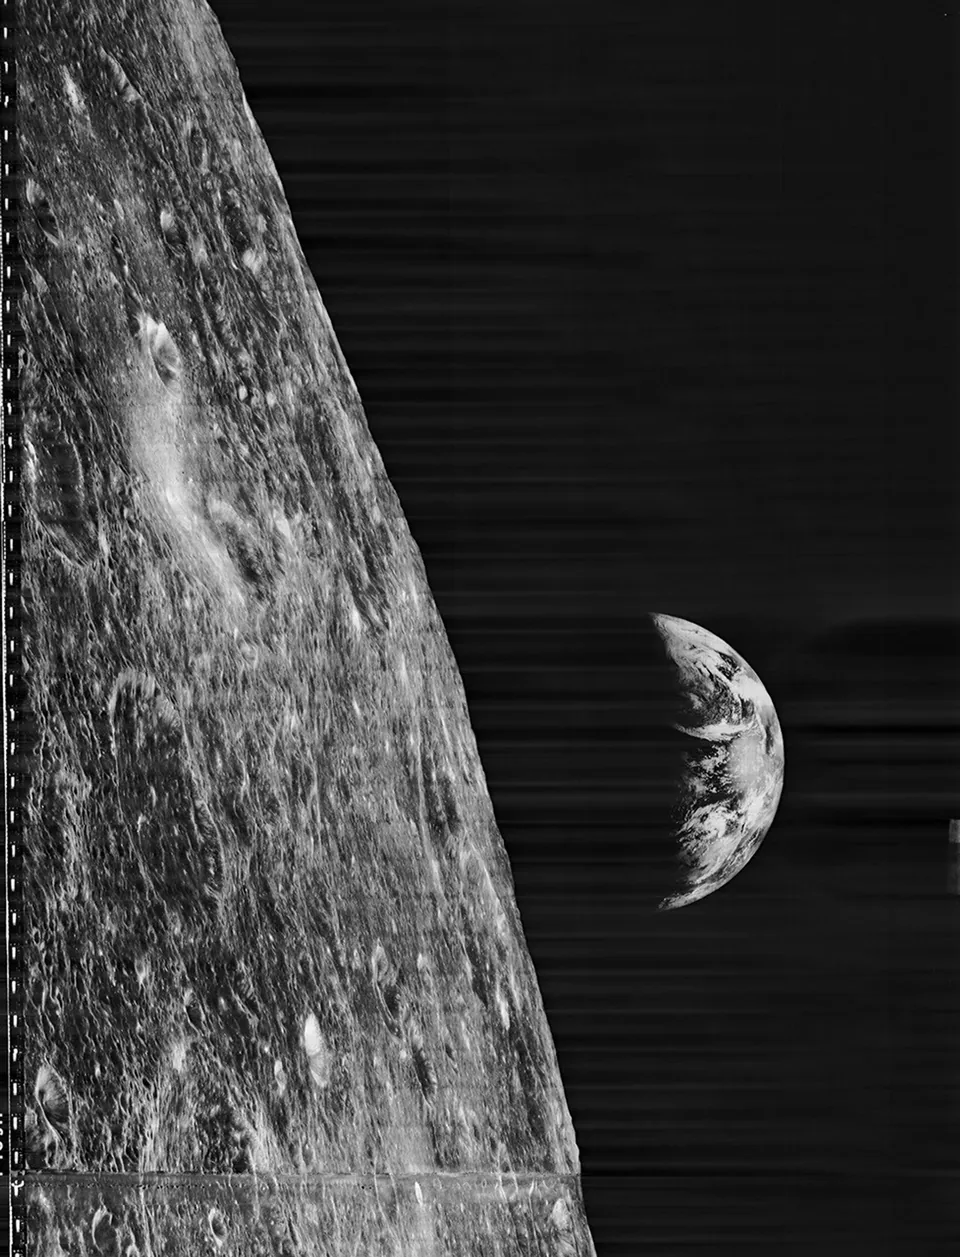
Indicadores y pruebas
| Indicador | Interpretación | Prueba necesaria |
|---|---|---|
| Archivo | La copia examinada | Referencia, fecha de consulta y hash |
| Leyenda | Atribución publicada por la fuente | Misión y crédito cotejados con la ficha |
| Derechos | Condiciones de reutilización, distintas de la autenticidad | Normas NASA, crédito y cambios de tamaño |
Ejemplo trabajado ficticio
Situación ilustrativa
Una imagen viral dice mostrar un evento reciente. El equipo busca la publicación más antigua, compara ubicaciones visibles y lee los metadatos de procedencia, si están presentes.
Decisión y pruebas esperadas
La nota separa lo que acredita la procedencia técnica, lo que confirman fuentes independientes y lo que aún no se puede concluir.
Indicadores de gestión
| Indicador | Qué mide | Primera acción |
|---|---|---|
| Procedencia | Artículos conectados a un origen documentado | Manejar pruebas decisivas sin una fuente primero |
| Corroboración | Conclusiones sustentadas en pistas independientes | Quitar repetición circular |
| Retardo de corrección | Tiempo desde que se descubre un error hasta que se actualiza el contenido | Mantener la lista de páginas dependientes |
| Incógnitas visibles | Limitaciones importantes declaradas explícitamente | Evitar que una hipótesis se convierta en un hecho |
Errores comunes
- Tratar el EXIF faltante como prueba de fabricación
- Parando después de una búsqueda inversa vacía
- Contabilización de republicaciones como fuentes independientes
- Corrigiendo una página pero no sus copias
Preguntas frecuentes
¿Los metadatos prueban que una imagen es genuina?
No. Se pueden eliminar, alterar o heredar de un dispositivo. Corrobóralos con contenido, contexto y procedencia.
¿Cómo se debe manejar el contenido sintético?
Busque información de procedencia disponible, examine la coherencia y el contexto, luego evalúe la veracidad de la afirmación asociada.
¿Se debe eliminar un error?
Corregir el contenido y su distribución de forma clara. Cuando ya ha influido en los lectores, una nota fechada explica mejor el cambio que una desaparición silenciosa.
Referencias: datos, usos y límites
Documentación consultada el .
Las notas detalladas de esta edición están disponibles en inglés.
| Fuente y finalidad | Dato o referencia verificada | Cómo utilizarla | Límite que debe conservarse |
|---|---|---|---|
| FIRST · Traffic Light Protocol Indicate who may receive redistributed information. |
TLP 2.0 uses RED, AMBER, GREEN and CLEAR; AMBER+STRICT restricts sharing to the recipient organisation. Labels must not be translated. | Keep the marking with the information and check recipients before forwarding. Ask the source to clarify any ambiguity. | TLP is neither a formal classification nor a reuse licence. It does not guarantee content accuracy. |
| C2PA · Content Credentials Describe and verify certain content provenance information. |
C2PA specification 2.4 defines manifests, assertions and cryptographic binding mechanisms associated with media. | Examine what the manifest asserts, who signed it and whether validation succeeds. Test preservation after transformations and distribution. | Validated provenance does not establish the truth of a scene. Absence of a manifest does not demonstrate a fake. |
Procedencia de medios y validación C2PA
Las notas detalladas de esta edición están disponibles en inglés.
A provenance report combines findings with different scopes. Signature, credential trust, content binding and scene context are separate assurances. Retain the exact asset and full report before summarising a result.
References use C2PA 2.4, dated April 2026 in its version history. This explorer explains twelve selected codes; it validates no file, retrieves no manifest and detects no AI-generated image. Cases are fictional and proposed checks are editorial guidance.
References consulted on .
Read twelve C2PA codes without overinterpreting them
The groups below are those used by the specification: success, informational and failure. A success code describes its particular check rather than replacing full validation. Missing information and a failed check cannot be reduced to a fake label.
| Code and group in C2PA 2.4 | Reported finding | Proposed follow-up | Conclusion to avoid |
|---|---|---|---|
claimSignature.validatedSuccess · success | The claim signature validated. | Also inspect trust, validity period and binding to the relevant asset. | The whole scene is true or every validation check is complete. |
signingCredential.trustedSuccess · success | The validator recognises the signing credential as trusted. | Record the trust list, its version and applied policy. | A signer’s name alone confirms the depicted event. |
timeStamp.validatedSuccess · success | The time-stamp token passes the checks described in the specification. | Distinguish it from capture time and inspect trust in the time-stamping authority. | The attested time necessarily dates the photographed scene. |
assertion.dataHash.matchSuccess · success | The data-hash binding matches within the checked scope. | Inspect the assertion, excluded ranges and any other applicable bindings. | Every byte and every metadata field is covered without exception. |
signingCredential.ocsp.inaccessibleInformation · informational | An online OCSP check was attempted without a response. | Retain network conditions and distinguish no response from a returned status. | The certificate is revoked, or certainly not revoked. |
signingCredential.ocsp.unknownInformation · informational | The OCSP response reports unknown for the signing credential. | Read the report and the policy used to handle that status. | Unknown means good or revoked. |
ingredient.unknownProvenanceInformation · informational | The relevant ingredient has no C2PA manifest. | Identify that ingredient and what its history actually makes available. | All ingredients were verified or that ingredient must be fake. |
assertion.dataHash.additionalExclusionsPresentInformation · informational | The binding excludes ranges beyond the C2PA Manifest Store. | Identify the excluded regions and their relevance to the claim being examined. | A hash success automatically protects excluded metadata. |
claimSignature.mismatchFailure · failure | Claim signature verification fails. | Retain asset, manifest and report; compare with the available source copy. | The cause of failure or somebody’s intent is already established. |
signingCredential.untrustedFailure · failure | The credential appears on none of the validator’s applicable trust lists. | Check policy and lists; distinguish this from a mathematically incorrect signature. | The file must be fabricated or its signature must be mathematically invalid. |
assertion.dataHash.mismatchFailure · failure | An asset byte range does not match the hash declared in the assertion. | Identify the checked copy and its transformations before explaining the difference. | Every difference establishes intentional falsification of the scene. |
signingCredential.ocsp.revokedFailure · failure | The OCSP response indicates revocation under the applied check. | Read the temporal evidence and validation procedure behind the result. | A summary detached from its date and report establishes the status of every copy. |
No code matches the filters.
Four version details useful to editorial and technical teams
- Published version
- The examples above follow C2PA 2.4, published in April 2026. Version 2.5, published in October 2026, expands support for asset formats and live media. Record your validator version and check the status-code table for the corresponding edition before interpreting a result.
- specVersion
- In this version the recommended field belongs in claim_generator_info. It is informational; validators should not change logic solely because of its value.
- crJSON
- This JSON-LD representation is a derived view of C2PA data for reporting and interoperability. It is not independently verifiable or a validation input format.
- c2pa.ai-disclosure
- The assertion carries an AI transparency declaration. It is not a universal detector, and its absence does not prove human origin.
Six fictional situations for a publication decision
| Fictional situation | Concrete check | Decision proportionate to evidence |
|---|---|---|
| A signed photo receives a new caption | Match the asset and report against the scene, date and location claimed by the new caption. | Describe checked provenance and leave the event attribution unresolved if uncorroborated. |
| A resized variant no longer matches the old binding | Compare original, transformation tool, distributed variant and manifest associated with each. | Handle the validation break without inferring malicious manipulation from the hash code alone. |
| Two validators do not trust the same signer | Record versions, trust lists and policy, then compare other findings. | Explain the trust-policy difference rather than treating it as contradictory truths about the scene. |
| A screenshot no longer presents a Content Credential | Seek the earlier asset and document the known copy chain. | Retain the screenshot’s status and incomplete history; an absent manifest does not establish a fake. |
| A binding success accompanies excluded metadata | Identify excluded fields or ranges and caption claims depending on them. | Limit the conclusion to covered data and verify decisive fields another way. |
| A supplier sends only a crJSON report | Request the asset and provenance data needed for verification, plus tool version and policy. | Examine the report without claiming to have repeated cryptographic validation. |
Retain a usable verification record
- Exact object
- Examined asset or stream, known origin, copy and transformations.
- Tool and policy
- Validator, version, configuration and relevant trust lists.
- Complete findings
- Codes, relevant object, explanations and time evidence; keep inconclusive information as well.
- Examined claim
- Exact statement about location, date, creator or AI use and its source.
- Editorial decision
- What is established, what is missing and what could change the conclusion.
Examine information origins and repetitions →
Primary sources and limits of this reader
This is not an exhaustive C2PA code inventory. Full procedures, formats and trust policies remain those of the specification and your validator. Diagrams, cases and records are CIE teaching proposals.
- C2PA · Content Credentials Technical Specification 2.4 · 2.4 · April 2026 ·
§5.3.1; §14.3; §15.2; §15.7–15.12 - C2PA · Content Credentials Technical Specification 2.5 · 2.5 · October 2026 ·
Appendix D and Appendix F.1 - C2PA · Content Credentials Explainer · 2.4
§2; §7.2–7.4 - C2PA · Security Considerations · 2.4
§2.2–2.6; §4; §5
Indicadores STIX y difusión TLP
Las notas detalladas de esta edición están disponibles en inglés.
Check TLP scope before publishing an excerpt
A traceable note does not by itself grant permission to redistribute it. TLP markings, additional restrictions and intended recipients must accompany a redaction or publication decision.
- AMBER+STRICT limits sharing to the organisation; AMBER’s scope for protecting clients does not apply by default.
- GREEN excludes public channels; CLEAR does not remove copyright rules or separate restrictions.
- Check the marking of each quoted field and obtain explicit source permission if the intended sharing exceeds the received scope.
Read the STIX, observations and TLP sharing reference →
Sources checked on · FIRST · TLP 2.0
OSINT: preservar las pruebas
Las notas detalladas de esta edición están disponibles en inglés.
Claimed provenance and preservation answer different questions
An edit history or manifest does not replace collection context. Preservation connects objects actually received, copies created and documented handling actions.
- Separate binary integrity, source identity and an assertion’s truthfulness.
- Keep derivative versions with their own identifiers and references.
- Document missing material before reaching a trust conclusion.
See copy lineage and the eight preservation cases →
Sources reviewed on · NIST · Digital Evidence Preservation · NIST IR 8387 · Full report · NIST · SP 800-86 · NIST SP 800-86 · Full report · NIST · FIPS 180-4 · Secure Hash Standard
PDF: expurgación y difusión
Las notas detalladas de esta edición están disponibles en inglés.
A documented transformation still needs release review
Derivative lineage explains technical provenance; it does not prove all excluded information was removed. Visible, hidden and embedded surfaces still need checking.
- Separate pending marks, applied redaction and hidden-data sanitization.
- Check a positive control before interpreting a negative search.
- Bind the decision to the delivered version and its recipients.
See surfaces and the pre-sharing review matrix →
Sources reviewed on · Adobe · Redacting and sanitizing PDFs · Adobe · Redact sensitive content · Adobe · Sanitize PDFs · ICO · Avoid accidental breaches when redacting · ICO · Hidden information in documents · Microsoft · Document Inspector
Cadenas de citas y escucha social
Las notas detalladas de esta edición están disponibles en inglés.
Separate origin, repost and corroboration
A capture or provenance signature may document a record without proving its claim. Before citing multiple publications, check whether they reference the same document.
- Keep the consulted version and its exact reference.
- Name missing citations instead of assuming their contents.
- Treat distinct documents as records to compare, without assuming independence.
Read the method and explore citation chains →
Government Communications · RESIST 3 · RESIST 3 · 2025 · consulted 2026-10-23
Government Communications · RESIST 3 quick reference · RESIST 3 · 2025 · consulted 2026-10-23
Referencias oficiales
Las referencias respaldan el método. Adapte los controles a su contexto; no constituyen certificación. Los títulos de referencia originales y los documentos fuente pueden estar en otro idioma.
Referencias consultadas el .
- C2PA — Content Credentials Technical Specification 2.5
- UC Berkeley / OHCHR — Berkeley Protocol on Digital Open Source Investigations
- FIRST · Traffic Light Protocol
- C2PA · Content Credentials
- C2PA · Content Credentials Explainer
- C2PA · Security Considerations
- NIST · Digital Evidence Preservation
- NIST IR 8387 · Full report
- NIST · SP 800-86
- NIST SP 800-86 · Full report
- NIST · FIPS 180-4 · Secure Hash Standard
- Adobe · Redacting and sanitizing PDFs
- Adobe · Redact sensitive content
- Adobe · Sanitize PDFs
- ICO · Avoid accidental breaches when redacting
- ICO · Hidden information in documents
- Microsoft · Document Inspector
- Government Communications · RESIST 3
- Government Communications · RESIST 3 quick reference

