
リソース · 10
情報の完全性:出所、コンテキスト、および変換を検証します。
文書、画像、または動画を引用、共有、または意思決定に使用する前に、その妥当性を確認する手順です。
更新済み · 16 min

このガイドが達成するのに役立つこと
- 最も古いアクセス可能なバージョンを見つける
- 本物のファイルと偽のキャプションを区別する
- 変換内容を文書化する
- 痕跡を消去せずに修正する
クイックチェック
- ファイルの公開者は誰で、どこから入手したのか?
- 以前のバージョンが存在するか?
- 場所と光の条件は一致しているか?
- メタデータは一貫しているが、十分とはみなされないか?
- どのコンテンツがこの証拠に依存しているか?
手順
- 1
アイテムを保存する
法的に認められている場合は、URL、アクセス日、受信ファイル、可視コンテキスト、ハッシュを保持する。 コピーを作成し、すべての変換を記録する。
成果物:ログエントリとハッシュ
- 2
出所追跡
最も古い公開元、主張されている作成者、中間リレー、トリミングまたは再圧縮されたバージョンを探す。
成果物:来歴チェーン
- 3
内容と文脈の確認
地形、建物、天候、影、言語、年代、既知の出来事を比較する。 本物の画像でも、場所や日付が偽装されている場合がある。
成果物:検証済みおよび却下された仮説
- 4
メタデータの検査
EXIF、エンコーディング、寸法、履歴を手がかりとして利用する。 これらの情報の有無だけで信憑性を証明することはできない。
成果物:解釈済みの技術記録
- 5
独立した裏付け
一次資料、別の角度からの映像、公式記録、または独立した目撃者を探す。 すべて同じファイルに基づいている重複箇所を特定する。
成果物:裏付けマトリックス
- 6
公開と訂正
確信度、限界、方法、情報源を明記する。 結論が変わった場合は、リンクされたページを更新し、日付入りの訂正メモを残す。
成果物:編集上の決定と訂正記録
理解し、計算し、判断する
実際の写真:ファイル、説明文、ページ日付を分ける
この「Earthrise」のNASAページはLunar Orbiter 1の画像と説明し、NASAを出典としています。ページの日付は撮影日を証明しません。タイトルだけでも探査ミッションを特定できません。
確認する主張を絞り、機関の出典ページに戻ります。参照先を保存し、表示上の変更を記録します。ハッシュはコピーの識別に使えますが、場面や解釈が真実であることまでは証明しません。
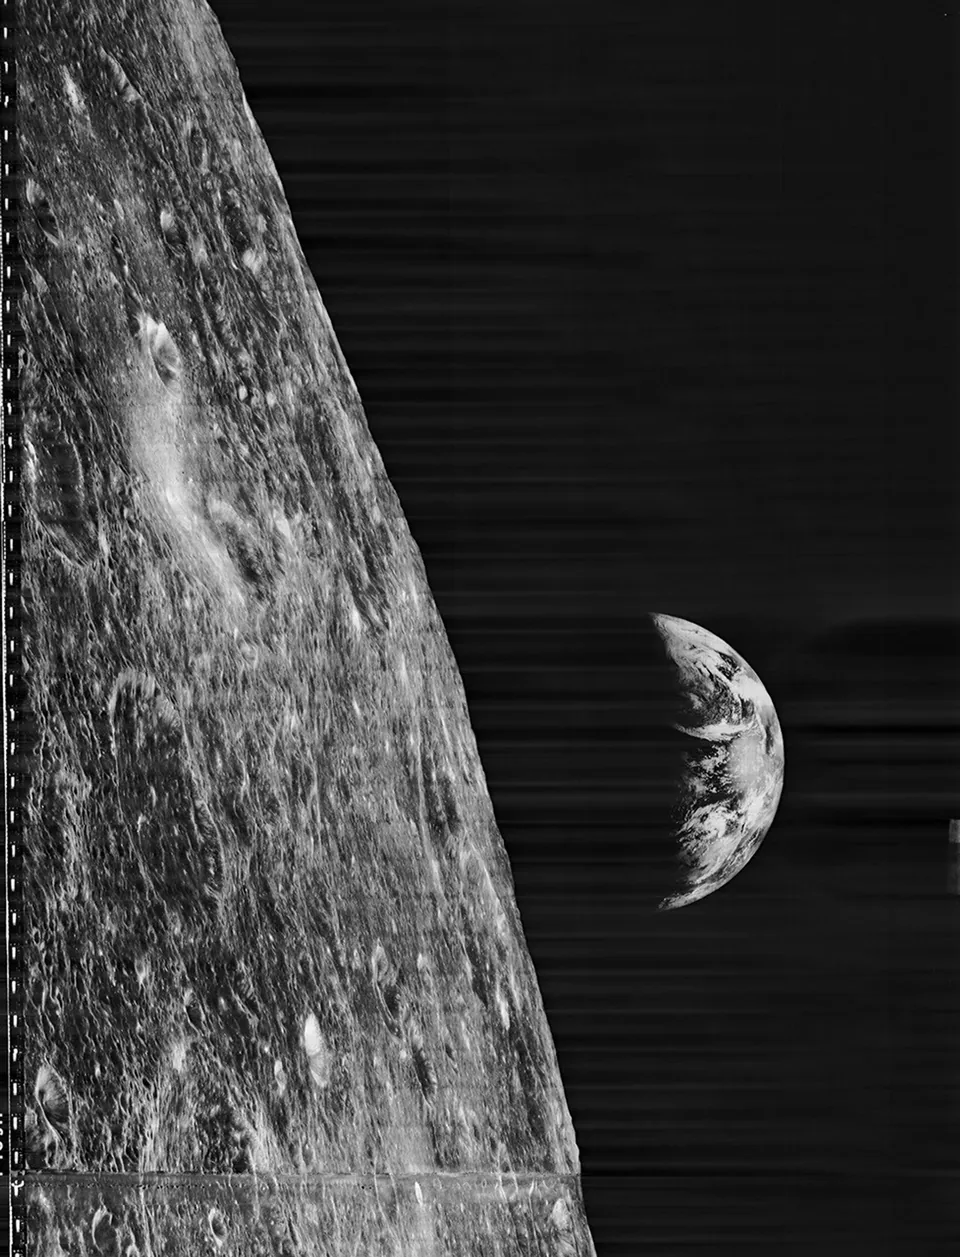
指標と確認資料
| 指標 | 読み取り方 | 必要な確認資料 |
|---|---|---|
| ファイル | 調べたコピー | 参照先、確認日、ハッシュ |
| 説明文 | 出典が公表した帰属情報 | ミッションとクレジットを出典ページと照合 |
| 利用条件 | 再利用条件と真正性は別の問題 | NASAの規定、クレジット、サイズ変更 |
架空の事例
具体的な状況
拡散した画像が最近の出来事を示していると主張している場合、チームは最も古い公開元を探し、表示されている場所を比較し、出所メタデータが存在する場合はそれを読み取る。
決定と期待される証拠
注記では、技術的な出所情報が証明するもの、独立した情報源が確認するもの、そしてまだ結論が出せないものを区別する。
管理指標
| 指標 | 測定対象 | 最初のアクション |
|---|---|---|
| 出所 | 文書化された出所に関連する項目 | 情報源が不明な決定的な証拠の取り扱い |
| 裏付け | 独立した手がかりによって裏付けられた結論 | 循環的な繰り返しの削除 |
| 修正の遅延 | エラーの発見からコンテンツの更新までの時間 | 依存ページリストの維持 |
| 目に見える不明点 | 重要な制限事項の明示 | 仮説が事実となることの防止 |
よくある間違い
- EXIF情報の欠落を捏造の証拠として扱う
- 逆検索が空の場合の停止
- 再掲載を独立した情報源としてカウントする
- 1ページのみを修正し、そのコピーは修正しない
よくある質問
メタデータは画像が本物であることを証明する?
いいえ。 メタデータは削除、変更、またはデバイスから継承される可能性があります。 内容、文脈、出所情報に基づいて裏付けを取る。
合成コンテンツはどのように扱うべきか?
入手可能な出所情報を探し、一貫性と文脈を検証した上で、関連する主張の真偽を評価する。
エラーは削除すべきか?
コンテンツとその配信を明確に修正する。 既に読者に影響を与えている場合は、日付入りの注記で変更内容を説明する方が、黙って削除するよりも効果的である。
参照資料:データ・用途・限界
資料確認日 .
この言語版の詳しい参照メモは英語で提供しています。
| 出典と目的 | 確認済みのデータ・指標 | 利用方法 | 留意する限界 |
|---|---|---|---|
| FIRST · Traffic Light Protocol Indicate who may receive redistributed information. |
TLP 2.0 uses RED, AMBER, GREEN and CLEAR; AMBER+STRICT restricts sharing to the recipient organisation. Labels must not be translated. | Keep the marking with the information and check recipients before forwarding. Ask the source to clarify any ambiguity. | TLP is neither a formal classification nor a reuse licence. It does not guarantee content accuracy. |
| C2PA · Content Credentials Describe and verify certain content provenance information. |
C2PA specification 2.4 defines manifests, assertions and cryptographic binding mechanisms associated with media. | Examine what the manifest asserts, who signed it and whether validation succeeds. Test preservation after transformations and distribution. | Validated provenance does not establish the truth of a scene. Absence of a manifest does not demonstrate a fake. |
メディアの来歴とC2PA検証
この言語版の詳しい参照メモは英語で提供しています。
A provenance report combines findings with different scopes. Signature, credential trust, content binding and scene context are separate assurances. Retain the exact asset and full report before summarising a result.
References use C2PA 2.4, dated April 2026 in its version history. This explorer explains twelve selected codes; it validates no file, retrieves no manifest and detects no AI-generated image. Cases are fictional and proposed checks are editorial guidance.
References consulted on .
Read twelve C2PA codes without overinterpreting them
The groups below are those used by the specification: success, informational and failure. A success code describes its particular check rather than replacing full validation. Missing information and a failed check cannot be reduced to a fake label.
| Code and group in C2PA 2.4 | Reported finding | Proposed follow-up | Conclusion to avoid |
|---|---|---|---|
claimSignature.validatedSuccess · success | The claim signature validated. | Also inspect trust, validity period and binding to the relevant asset. | The whole scene is true or every validation check is complete. |
signingCredential.trustedSuccess · success | The validator recognises the signing credential as trusted. | Record the trust list, its version and applied policy. | A signer’s name alone confirms the depicted event. |
timeStamp.validatedSuccess · success | The time-stamp token passes the checks described in the specification. | Distinguish it from capture time and inspect trust in the time-stamping authority. | The attested time necessarily dates the photographed scene. |
assertion.dataHash.matchSuccess · success | The data-hash binding matches within the checked scope. | Inspect the assertion, excluded ranges and any other applicable bindings. | Every byte and every metadata field is covered without exception. |
signingCredential.ocsp.inaccessibleInformation · informational | An online OCSP check was attempted without a response. | Retain network conditions and distinguish no response from a returned status. | The certificate is revoked, or certainly not revoked. |
signingCredential.ocsp.unknownInformation · informational | The OCSP response reports unknown for the signing credential. | Read the report and the policy used to handle that status. | Unknown means good or revoked. |
ingredient.unknownProvenanceInformation · informational | The relevant ingredient has no C2PA manifest. | Identify that ingredient and what its history actually makes available. | All ingredients were verified or that ingredient must be fake. |
assertion.dataHash.additionalExclusionsPresentInformation · informational | The binding excludes ranges beyond the C2PA Manifest Store. | Identify the excluded regions and their relevance to the claim being examined. | A hash success automatically protects excluded metadata. |
claimSignature.mismatchFailure · failure | Claim signature verification fails. | Retain asset, manifest and report; compare with the available source copy. | The cause of failure or somebody’s intent is already established. |
signingCredential.untrustedFailure · failure | The credential appears on none of the validator’s applicable trust lists. | Check policy and lists; distinguish this from a mathematically incorrect signature. | The file must be fabricated or its signature must be mathematically invalid. |
assertion.dataHash.mismatchFailure · failure | An asset byte range does not match the hash declared in the assertion. | Identify the checked copy and its transformations before explaining the difference. | Every difference establishes intentional falsification of the scene. |
signingCredential.ocsp.revokedFailure · failure | The OCSP response indicates revocation under the applied check. | Read the temporal evidence and validation procedure behind the result. | A summary detached from its date and report establishes the status of every copy. |
No code matches the filters.
Four version details useful to editorial and technical teams
- Published version
- The examples above follow C2PA 2.4, published in April 2026. Version 2.5, published in October 2026, expands support for asset formats and live media. Record your validator version and check the status-code table for the corresponding edition before interpreting a result.
- specVersion
- In this version the recommended field belongs in claim_generator_info. It is informational; validators should not change logic solely because of its value.
- crJSON
- This JSON-LD representation is a derived view of C2PA data for reporting and interoperability. It is not independently verifiable or a validation input format.
- c2pa.ai-disclosure
- The assertion carries an AI transparency declaration. It is not a universal detector, and its absence does not prove human origin.
Six fictional situations for a publication decision
| Fictional situation | Concrete check | Decision proportionate to evidence |
|---|---|---|
| A signed photo receives a new caption | Match the asset and report against the scene, date and location claimed by the new caption. | Describe checked provenance and leave the event attribution unresolved if uncorroborated. |
| A resized variant no longer matches the old binding | Compare original, transformation tool, distributed variant and manifest associated with each. | Handle the validation break without inferring malicious manipulation from the hash code alone. |
| Two validators do not trust the same signer | Record versions, trust lists and policy, then compare other findings. | Explain the trust-policy difference rather than treating it as contradictory truths about the scene. |
| A screenshot no longer presents a Content Credential | Seek the earlier asset and document the known copy chain. | Retain the screenshot’s status and incomplete history; an absent manifest does not establish a fake. |
| A binding success accompanies excluded metadata | Identify excluded fields or ranges and caption claims depending on them. | Limit the conclusion to covered data and verify decisive fields another way. |
| A supplier sends only a crJSON report | Request the asset and provenance data needed for verification, plus tool version and policy. | Examine the report without claiming to have repeated cryptographic validation. |
Retain a usable verification record
- Exact object
- Examined asset or stream, known origin, copy and transformations.
- Tool and policy
- Validator, version, configuration and relevant trust lists.
- Complete findings
- Codes, relevant object, explanations and time evidence; keep inconclusive information as well.
- Examined claim
- Exact statement about location, date, creator or AI use and its source.
- Editorial decision
- What is established, what is missing and what could change the conclusion.
Examine information origins and repetitions →
Primary sources and limits of this reader
This is not an exhaustive C2PA code inventory. Full procedures, formats and trust policies remain those of the specification and your validator. Diagrams, cases and records are CIE teaching proposals.
- C2PA · Content Credentials Technical Specification 2.4 · 2.4 · April 2026 ·
§5.3.1; §14.3; §15.2; §15.7–15.12 - C2PA · Content Credentials Technical Specification 2.5 · 2.5 · October 2026 ·
Appendix D and Appendix F.1 - C2PA · Content Credentials Explainer · 2.4
§2; §7.2–7.4 - C2PA · Security Considerations · 2.4
§2.2–2.6; §4; §5
STIX指標とTLPによる共有
この言語版の詳しい参照メモは英語で提供しています。
Check TLP scope before publishing an excerpt
A traceable note does not by itself grant permission to redistribute it. TLP markings, additional restrictions and intended recipients must accompany a redaction or publication decision.
- AMBER+STRICT limits sharing to the organisation; AMBER’s scope for protecting clients does not apply by default.
- GREEN excludes public channels; CLEAR does not remove copyright rules or separate restrictions.
- Check the marking of each quoted field and obtain explicit source permission if the intended sharing exceeds the received scope.
Read the STIX, observations and TLP sharing reference →
Sources checked on · FIRST · TLP 2.0
OSINT:証拠の保全
この言語版の詳しい参照メモは英語で提供しています。
Claimed provenance and preservation answer different questions
An edit history or manifest does not replace collection context. Preservation connects objects actually received, copies created and documented handling actions.
- Separate binary integrity, source identity and an assertion’s truthfulness.
- Keep derivative versions with their own identifiers and references.
- Document missing material before reaching a trust conclusion.
See copy lineage and the eight preservation cases →
Sources reviewed on · NIST · Digital Evidence Preservation · NIST IR 8387 · Full report · NIST · SP 800-86 · NIST SP 800-86 · Full report · NIST · FIPS 180-4 · Secure Hash Standard
PDF:墨消しと共有
この言語版の詳しい参照メモは英語で提供しています。
A documented transformation still needs release review
Derivative lineage explains technical provenance; it does not prove all excluded information was removed. Visible, hidden and embedded surfaces still need checking.
- Separate pending marks, applied redaction and hidden-data sanitization.
- Check a positive control before interpreting a negative search.
- Bind the decision to the delivered version and its recipients.
See surfaces and the pre-sharing review matrix →
Sources reviewed on · Adobe · Redacting and sanitizing PDFs · Adobe · Redact sensitive content · Adobe · Sanitize PDFs · ICO · Avoid accidental breaches when redacting · ICO · Hidden information in documents · Microsoft · Document Inspector
引用の連鎖とソーシャルリスニング
この言語版の詳しい参照メモは英語で提供しています。
Separate origin, repost and corroboration
A capture or provenance signature may document a record without proving its claim. Before citing multiple publications, check whether they reference the same document.
- Keep the consulted version and its exact reference.
- Name missing citations instead of assuming their contents.
- Treat distinct documents as records to compare, without assuming independence.
Read the method and explore citation chains →
Government Communications · RESIST 3 · RESIST 3 · 2025 · consulted 2026-10-23
Government Communications · RESIST 3 quick reference · RESIST 3 · 2025 · consulted 2026-10-23
公式参照文献
参照文献はメソッドを裏付けるものです。 チェックは状況に合わせて調整してください。 これらは認証ではありません。 元の参照文献のタイトルやソース文書は別の言語で書かれている場合があります。
参照資料の確認日 .
- C2PA — Content Credentials Technical Specification 2.5
- UC Berkeley / OHCHR — Berkeley Protocol on Digital Open Source Investigations
- FIRST · Traffic Light Protocol
- C2PA · Content Credentials
- C2PA · Content Credentials Explainer
- C2PA · Security Considerations
- NIST · Digital Evidence Preservation
- NIST IR 8387 · Full report
- NIST · SP 800-86
- NIST SP 800-86 · Full report
- NIST · FIPS 180-4 · Secure Hash Standard
- Adobe · Redacting and sanitizing PDFs
- Adobe · Redact sensitive content
- Adobe · Sanitize PDFs
- ICO · Avoid accidental breaches when redacting
- ICO · Hidden information in documents
- Microsoft · Document Inspector
- Government Communications · RESIST 3
- Government Communications · RESIST 3 quick reference

