Possible deliverables
Possible deliverables
- Sourced OSINT dossier
- Entity and alias mapping
- Timeline and confidence grid
- Risk note and direct verification points

04 / 06
Cyber · AI · Digital intelligence
Assess a third party, a presence or a digital situation before a sensitive commitment.
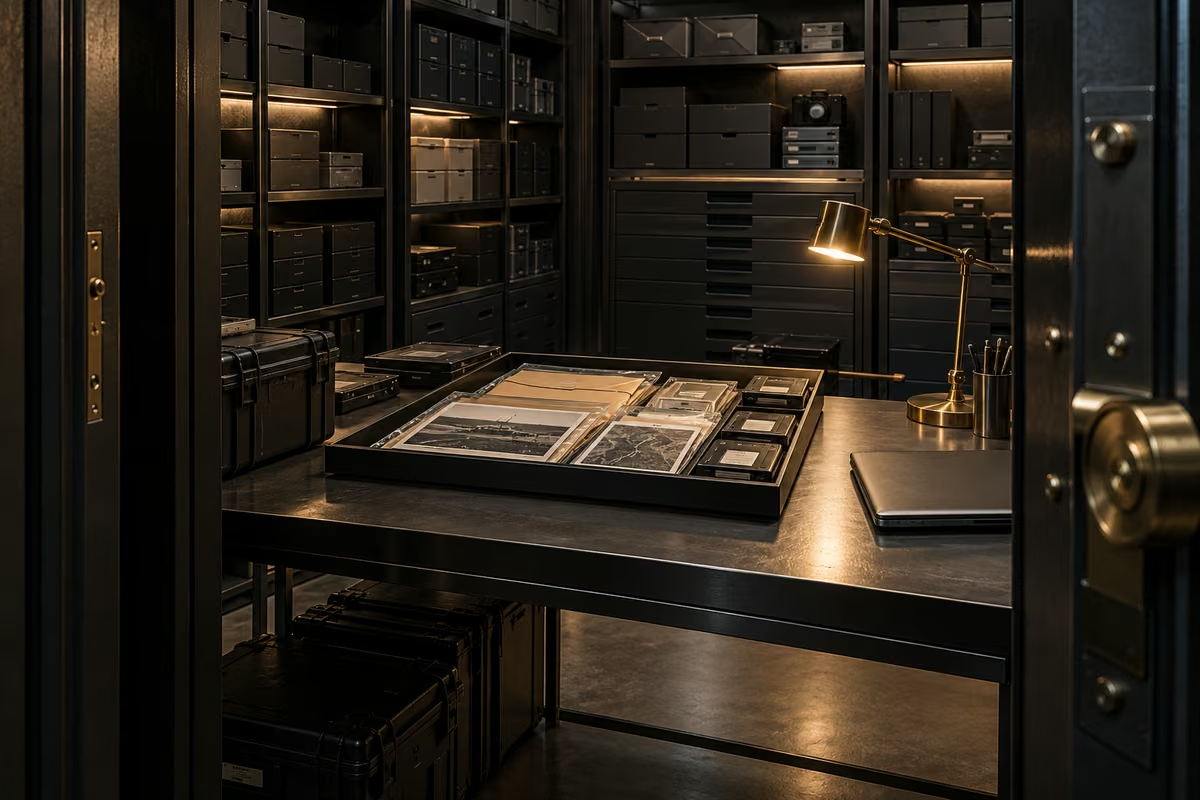
Accessible information is traced to its source, dated, corroborated and placed in context. The deliverable clearly separates established facts, credible signals, hypotheses and unknowns.
04
How the assignment works
A short, explicit process adapted to the sensitivity of the situation.
We define the decision to support, relevant assets, constraints, authorised sources and required confidentiality.
Collection and analysis follow the agreed scope. Facts, hypotheses and areas of uncertainty remain clearly separated.
Each finding is assessed by reliability, likely impact and the effort required to act.
You receive a readable synthesis, useful evidence and a roadmap that can be put into practice.
Possible deliverables
Common situations
Use these examples to agree on a verifiable deliverable. Checks and thresholds follow the agreed scope; the examples below are not client results.
| What to check | Evidence to request | Decision it supports |
|---|---|---|
| Third-party identity | Contracting entity, identifiers, jurisdiction and separation of namesakes; dated records. | Avoid assigning another entity’s references or incidents to the assessed provider. |
| Decisive claim | Claim, primary source, covered period, possible contradiction and direct confirmation still needed. | Accept sufficient evidence or set a condition before commitment. |
| Dependencies | Subprocessors, sensitive access, essential services and declared responsibilities; unverified items distinguished. | Identify the failure point or dependency that would change the choice. |
| Exit and full cost | Cost assumptions, portability, export format, owners and an exit scenario to exercise. | Compare options across their usable lifetime and exit, rather than entry price alone. |
Put the decision to the test
Before onboarding a supplier, a team receives commercial and technical records. Two name an entity different from the one in the proposed contract.
Fictional teaching case. Figures explain the reasoning; they are neither client results nor thresholds required by a standard.
| Possible choice | Missing evidence or supporting reason |
|---|---|
| Approve based on document volume | Quantity does not resolve an identity mismatch. |
| Immediately conclude fraud | A subsidiary, name change or outdated record may explain a difference. |
| Hold the conclusion on affected points | Establish the relationship between entities and request an up-to-date record. |
The summary describes the inconsistency without inferring intent. It separates established facts, the supplier’s explanation and outstanding checks. The contractual decision must account for the unresolved issue and its effect on delivery.
Select a claim that conditions signature and trace its entity, period and supporting record. If the evidence scope excludes the service being purchased, retain an unresolved condition before commitment.
An authentic document can concern a different entity or scope. Documentary consistency does not guarantee future service quality.
This UK public procurement guide connects strategy, lifecycle costs and exit. It offers comparison principles; the proposed conditions still need to fit the contract and context.
References checked on 15 October 2026.
Before the assignment
Verification follows the contemplated commitment: a purchase, partnership and dispute need different evidence. The record bounds entities, periods and lawfully accessible information, and preserves contradictions. The dossier connects each decisive claim to an entity, date, document and verification limit. It examines technical dependencies, subprocessors, access, reversibility and claimed continuity. Public evidence is cross-checked with authorised provider responses. Unknowns stay visible and can become decision conditions rather than unsupported reassuring conclusions.
Documentation reviewed on .
| Source and purpose | Verified data or benchmark | How to use it | Limitation to retain |
|---|---|---|---|
| NIST · Cybersecurity Framework Structure the outcomes expected from a cybersecurity programme. |
CSF 2.0 has six functions: Govern, Identify, Protect, Detect, Respond and Recover. It does not prescribe a single way to achieve outcomes. | Describe current and target profiles with evidence, gaps and owners. Connect each priority to the services it helps protect. | Mapping to the framework is neither certification nor proof that every control works. |
| SPDX · Specifications Describe components and information in a software bill of materials. |
The official specifications page distinguishes SPDX 3.0 from earlier versions such as 2.3. Document version affects schema and tool compatibility. | Request format, version, build scope and component identifiers. Compare the bill of materials with the delivered artefact. | A bill of materials alone proves neither vulnerability absence, dependency completeness nor compliance with every licence. |
| OWASP · CycloneDX Exchange bills of materials and supply-chain information. |
The official overview dates specification 1.7 to 21 October 2025 and documents JSON, XML and Protobuf. | Check version, component references and dependency links. Retain the connection between the bill of materials, build and deployed product. | Changing format does not fix missing components. A descriptive inventory and a vulnerability impact assessment answer different questions. |
A document signature or image provenance alone establishes neither operational capacity, a customer reference nor the reality of a depicted site. Relate the item to the actual claim being examined.
Open the C2PA explorer and publication cases →
References consulted on · C2PA · Content Credentials Explainer ODNI · ICD 203, Analytic Standards
A supplier may provide an SBOM and VEX document whose scope does not match your build. Connect those records to the vulnerability, delivered version and explicit status conditions.
Read VEX statuses and applicability conditions →
Sources checked on · OpenVEX · Specification v0.2.0
A digital-trust dossier must show which checks covered which copy. A result grid replaces neither content inspection nor checks on access and accessible versions.
See surfaces and the pre-sharing review matrix →
Sources reviewed on · Adobe · Redacting and sanitizing PDFs · Adobe · Redact sensitive content · Adobe · Sanitize PDFs · ICO · Avoid accidental breaches when redacting · ICO · Hidden information in documents · Microsoft · Document Inspector
FAQ
Practical answers to help frame the need before an initial conversation.
The assignment uses lawful open sources and authorised documents: registers, publications, domains, digital presence, historical records and publicly documented relationships.
It reduces uncertainty without inventing what sources cannot establish. The report separates facts, signals, contradictions and checks that still need to be conducted directly.
Reconcile the legal name, registry identifier or LEI where available, jurisdiction and dates. Distinguish company, subsidiary and brand before attributing adverse information. Keep an unresolved identity as an explicit uncertainty rather than merging dossiers. An identifier helps recognise an entity; it does not establish trustworthiness.
Digital ecosystem
 Française du Numérique
Web creation, SEO and content
francaise-du-numerique.fr
ENExplore
 French Digital Society
Digital professions and expertise
french-digital-society.com
ENExplore
 Internet Intelligence Service
OSINT, monitoring and due diligence
internet-intelligence-service.com
ENExplore
 CFSN
Digital support for small businesses
cfsn.fr
French editionExplore
 World Affiliate Guide
Affiliate and performance marketing
world-affiliate-guide.com
ENExplore
 World Social Networks
Social networks, usage and privacy
world-social-networks.com
ENExplore
 World Web Certified
Curated web directory and guides
worldwebcertified.com
ENExplore