Guides · Methods · Open data
Digital intelligence resource centre
Resources built to turn a complex topic into a documented decision: practical steps, expected evidence, useful indicators and reusable controls.
- 118
- in-depth guides
- 315
- verifiable controls
- 4
- maturity levels
Quick reference
Key concepts, clearly explained
Security, AI, measurement, indexing, forms, APIs, email and moderation: concepts connected to the resource centre’s practical guides.
Reading paths
Choose a starting point for your decision
These paths connect guides that work together. You can also browse the complete library directly.
Establish the facts
Start from traceable sources, verify information and qualify dependencies before deciding.
Prepare response and recovery
Identify exposed assets, triage an incident signal and prove that the service can return.
Build a usable service
Connect speed, security, accessibility and integration continuity to actual user journeys.
Deploy AI with evidence
Choose a use, evaluate answers and retain control of data, actions and suppliers.
Reduce entry paths
Remediate vulnerabilities found on actual assets and strengthen sign-in without leaving weak recovery paths.
Measure and decide
Define events, respect privacy choices and run an interpretable experiment.
Make commerce journeys reliable
Check published offers and verify that a task remains complete in every language.
Detect with evidence
Connect technical records to useful signals and a rehearsed response.
Keep pages findable and useful
Diagnose crawling and indexing, then maintain accurate content that meets a real need.
Make every interaction reliable
Help people recover from form errors, evolve API contracts and verify email sending.
Care for communities
Use clear rules and proportionate escalation for sensitive situations.
Secure data graphs
Test permissions, query cost and each field’s exposure before opening a GraphQL API.
Align sold variants
Connect catalog, URL, published offer and cart for every available option.
Diagnose real experience
Start from observed visits, then reproduce responsible interactions and elements.
Triage public signals
Keep provenance, check facts and route sensitive cases.
Updated 12 October 2026
118 guides to frame, verify and act
Each guide works independently or with the shared matrix to prepare an assessment, workshop or roadmap.
118 / 118 guides shown. Search also covers questions, methods and comparisons.
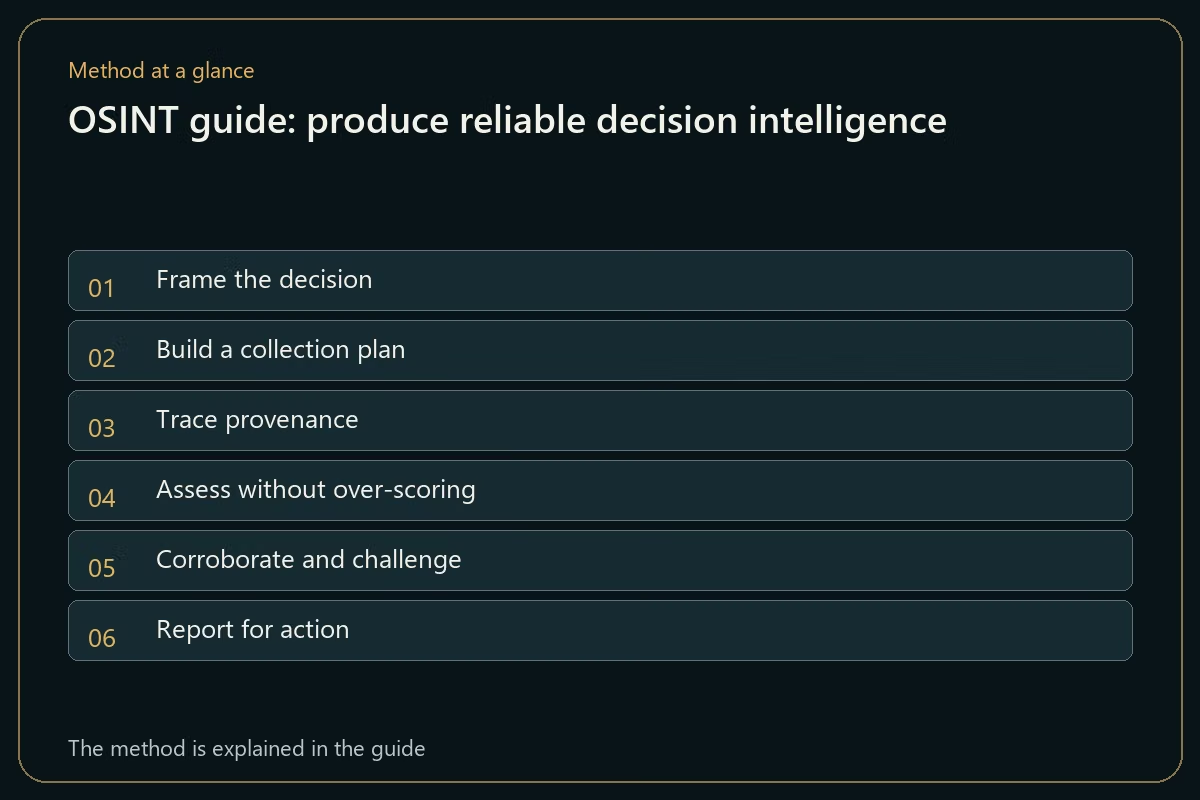
OSINT guide: produce reliable decision intelligence
A six-step method for turning scattered open sources into a traceable, nuanced and actionable brief.
Read the guide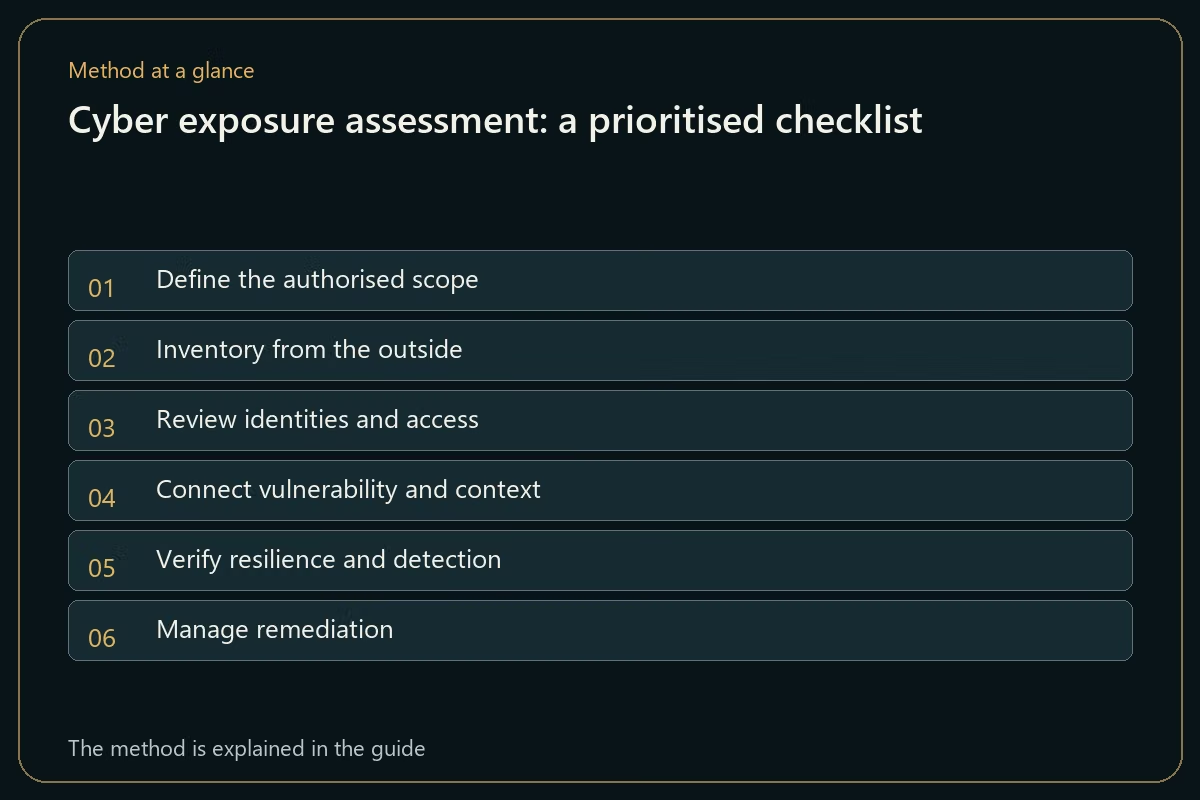
Cyber exposure assessment: a prioritised checklist
Inventory what is visible, connect exposure to business assets and turn findings into a verifiable risk-reduction plan.
Read the guide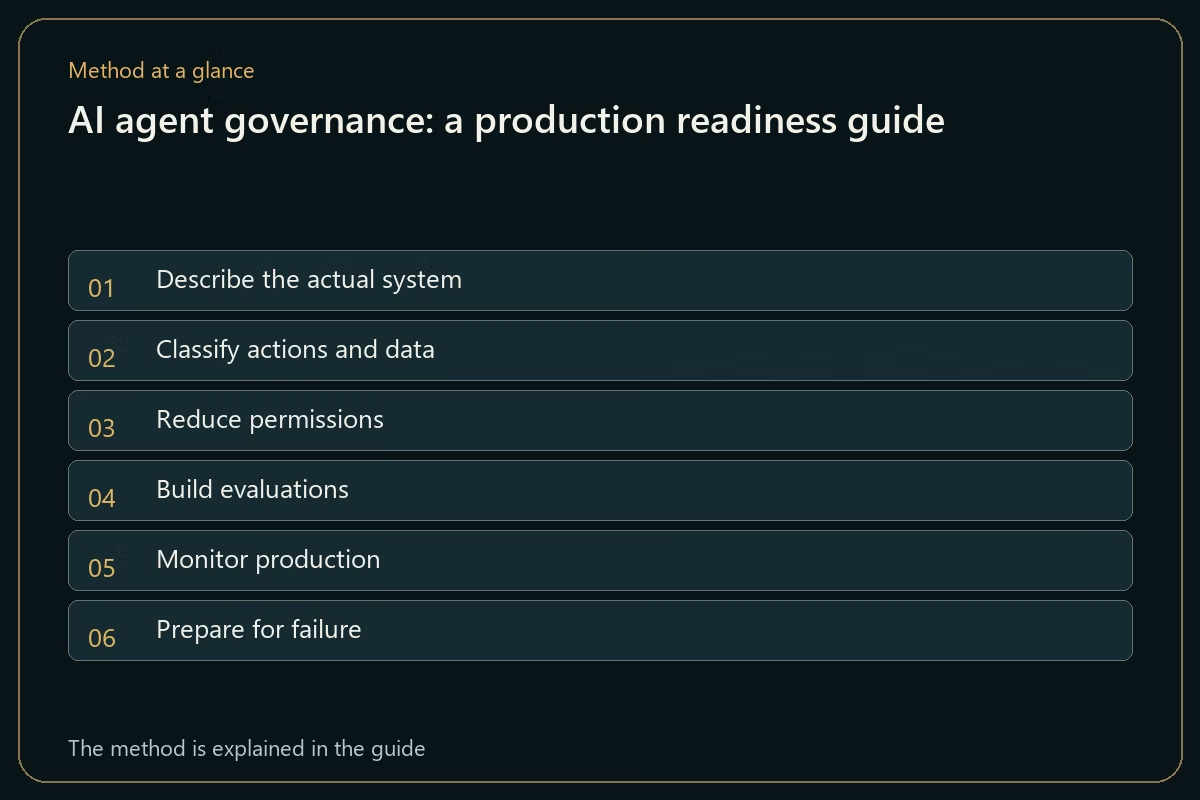
AI agent governance: a production readiness guide
Frame permissions, data, tests, oversight and shutdown before an agent is trusted with a business process.
Read the guide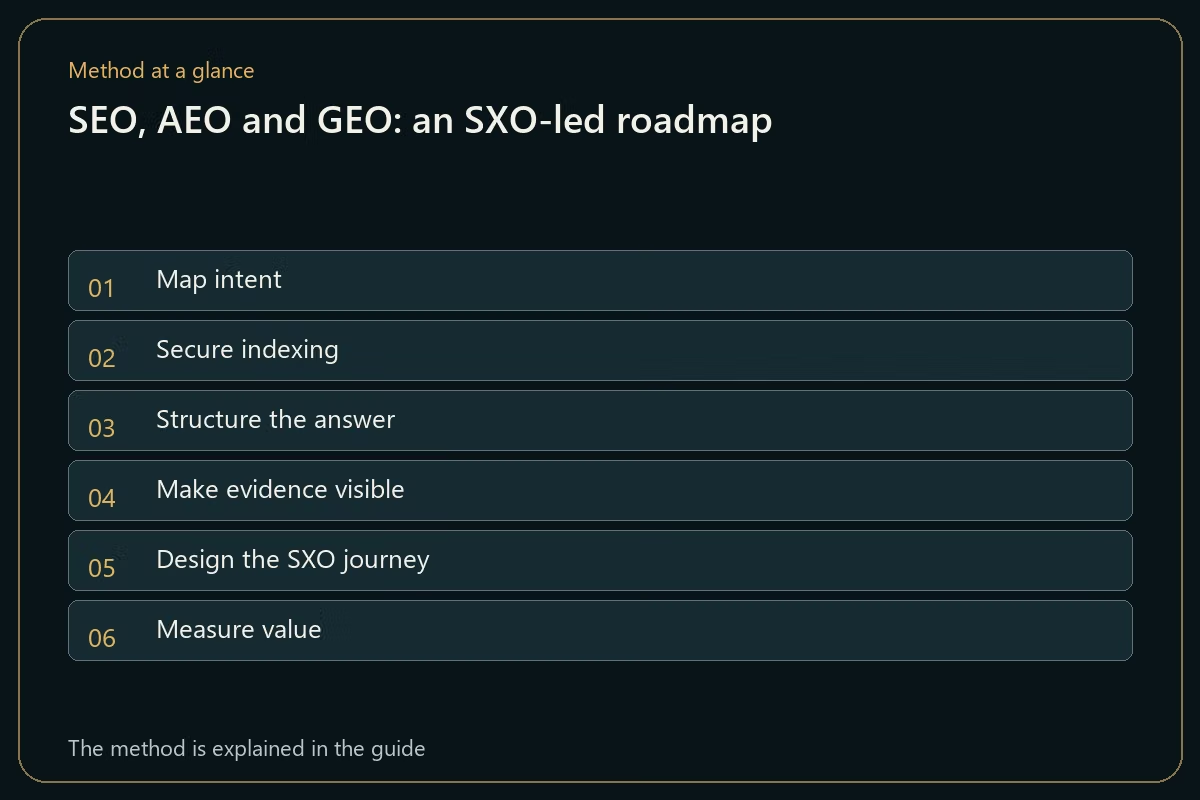
SEO, AEO and GEO: an SXO-led roadmap
Connect indexing, direct answers, citation readiness and conversion in one measurable content architecture.
Read the guide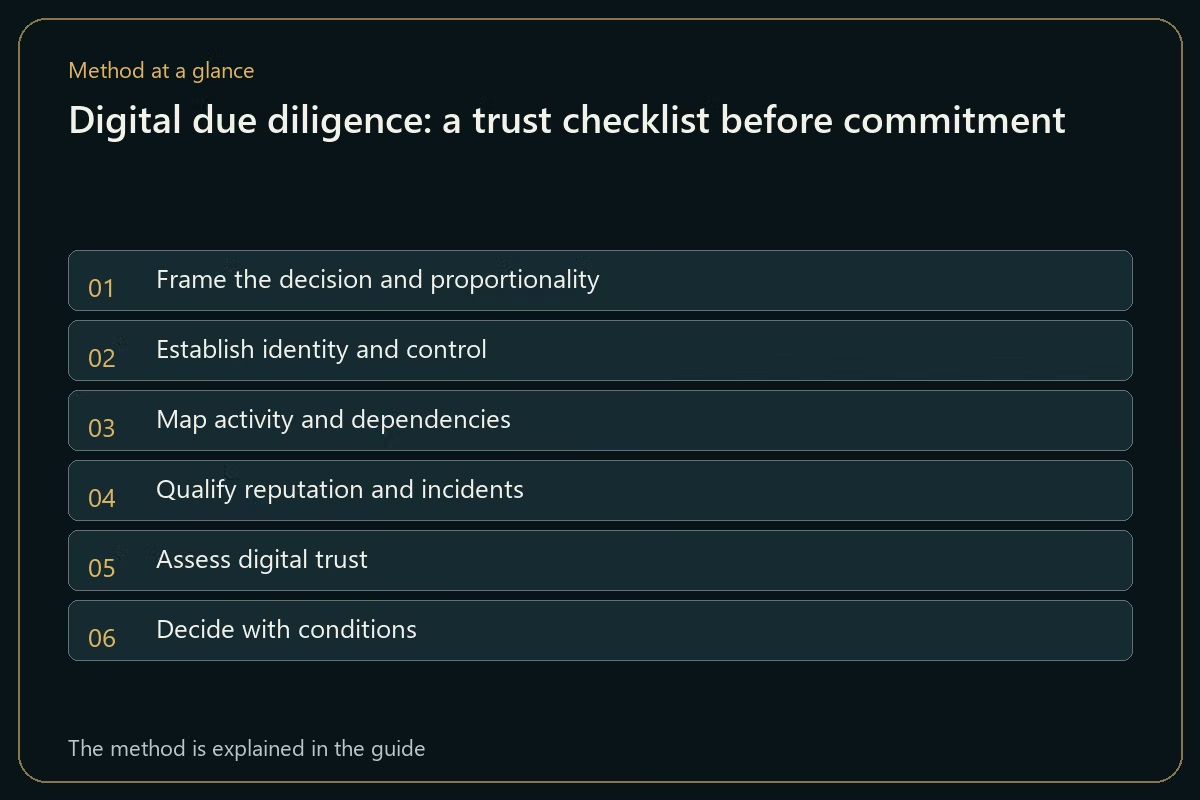
Digital due diligence: a trust checklist before commitment
Verify an organisation, its leadership, dependencies and risk signals without turning the investigation into indiscriminate data collection.
Read the guide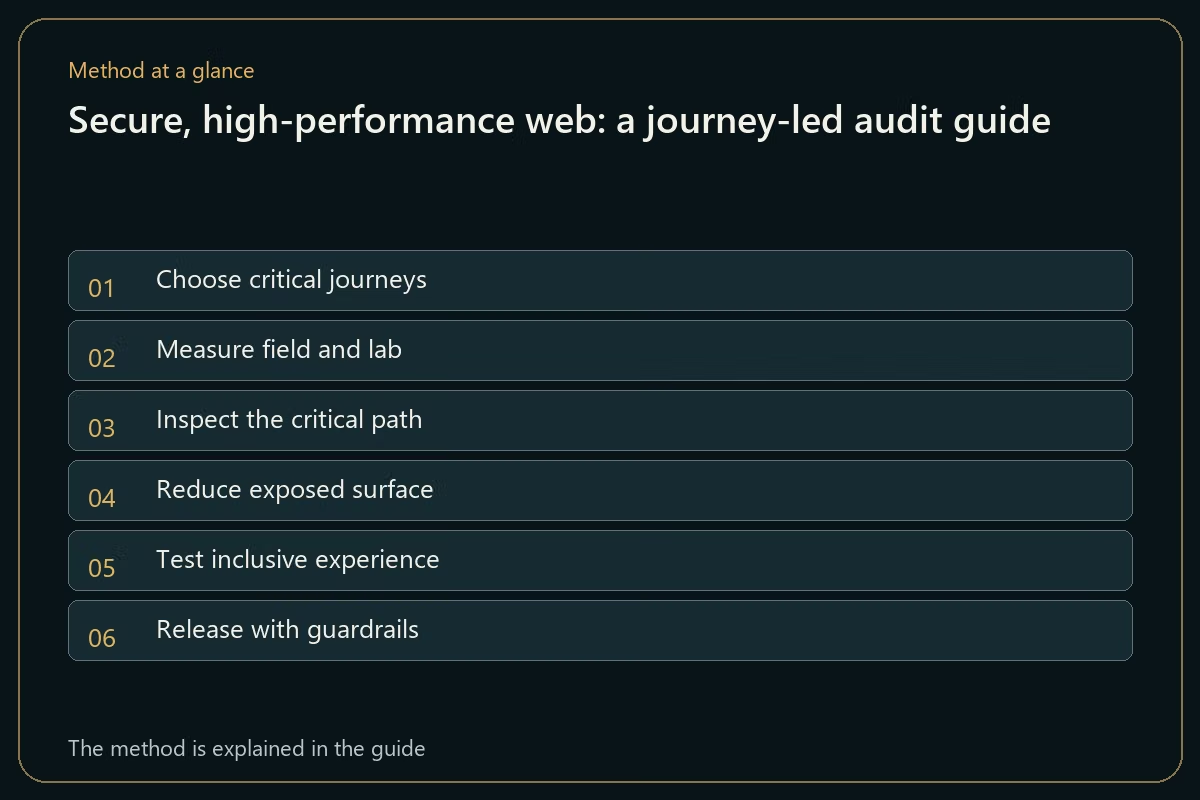
Secure, high-performance web: a journey-led audit guide
Audit speed, accessibility, security and conversion around the actions users genuinely need to complete.
Read the guide
Third-party digital risk: assess a critical supplier
Connect evidence, dependencies, subcontractors, continuity and reversibility before entrusting a sensitive service or dataset.
Read the guide
Cyber incident exercise: test decisions before the crisis
Build a realistic scenario that tests coordination, continuity, evidence, communication and service recovery without disrupting production.
Read the guide
RAG quality: evaluate a knowledge assistant with evidence
Measure corpus, retrieval, citations, answers, abstention and drift separately so that you know what genuinely needs fixing.
Read the guide
Information integrity: verify provenance, context and transformations
A procedure for qualifying a document, image or video before citing, sharing or using it in a decision.
Read the guide
Identity and account recovery: govern the complete lifecycle
Connect account creation, change, privileges, recovery and closure to verifiable evidence and rehearsed decisions.
Read the guide
Multilingual SEO: architecture, hreflang and editorial quality
Build discoverable, coherent and genuinely useful language editions without multiplying duplicates or conflicting signals.
Read the guide
Data lifecycle governance: retain, archive and delete with evidence
Connect every data category to a purpose, owner, retention trigger and deletion process that can actually be verified.
Read the guide
AI vendor evaluation: evidence, dependencies and exit conditions
A selection framework for testing real quality, qualifying data flows and preserving a practical exit option.
Read the guide
Measure visibility in AI-assisted search
Track appearances, citations, visits and outcomes without confusing observed visibility with causal impact.
Read the guide
Software supply chain assurance: components to release
Connect components, provenance, builds, vulnerabilities and updates to each release actually deployed.
Read the guide
Govern domains and rehearse DNS recovery
Inventory domains, protect registrar access and test recovery of naming services.
Read the guide
Make API integrations resilient to outages
Map dependencies, bound retries and keep essential journeys usable during external failures.
Read the guide
Review browser extensions before enterprise deployment
Assess permissions, site access, updates and the ability to remove an extension.
Read the guide
Test a backup restoration from copy to working service
Move from assumed backup availability to a rehearsed and documented recovery.
Read the guide
Triage a cyber incident and preserve early evidence
Turn a confusing signal into a timeline, hypotheses, decisions and proportionate escalation.
Read the guide
Evaluate web accessibility through journeys and evidence
Set a scope, test essential tasks and document fixes that can be verified.
Read the guide
Prioritize vulnerabilities and verify remediation
Connect known exploitation, exposed assets, business impact and proof of a working fix.
Read the guide
Deploy phishing-resistant authentication with safe recovery
Use factors bound to the genuine service and protect enrollment, loss and revocation.
Read the guide
Build an event measurement plan and verify collection
Move from a decision need to an event dictionary, scenario tests and discrepancy monitoring.
Read the guide
Run an A/B experiment that supports a sound decision
Specify hypothesis, assignment, primary metric and guardrails before comparing variants.
Read the guide
Measure audiences while respecting privacy choices
Audit trackers, purposes, configuration and refusal journeys before publishing metrics.
Read the guide
Improve multichannel product catalog data quality
Reconcile offers, variants, images, prices and stock across page, feed and structured data.
Read the guide
Make security event logs ready for detection
Choose events, protect records, correlate systems and rehearse the response.
Read the guide
QA multilingual content and complete user journeys
Check languages, alternates, forms, formats and RTL screens beyond translated body copy.
Read the guide
Diagnose crawling and indexing of useful pages
Connect links, HTTP responses, directives, canonicals and Search Console evidence before fixing.
Read the guide
Design accessible forms and recoverable errors
Guide entry, explain failure and preserve a person’s progress through the task.
Read the guide
Evolve API contracts without losing clients
Describe requests, responses and errors; test versions and make webhooks safe to replay.
Read the guide
Improve email sender trust and deliverability
Check sender identity, message classes, unsubscribe behavior and rejection causes.
Read the guide
Govern and maintain a useful content library
Tie each page to a need, source, owner and review decision.
Read the guide
Moderate a community and escalate sensitive cases
Publish rules, triage messages, respond consistently and rehearse urgent scenarios.
Read the guide
Secure a GraphQL API: authorization, query cost and evidence
Enforce object and field rights, bound server work and test denial paths.
Read the guide
Keep product variants consistent from URL to cart
Align selected option, identity, image, price, stock, markup and purchase.
Read the guide
Diagnose Core Web Vitals in field data
Connect LCP, INP and CLS to actual elements and interactions before fixing.
Read the guide
Triage social listening signals before acting
Separate volume, origins, reposts and verified facts to route useful cases.
Read the guide
Coordinated vulnerability disclosure: receive, fix and inform
Build a safe route for external reports, assess impact, coordinate affected parties and publish useful guidance.
Read the guide
Accessible conversational assistants: multiple modes, recovery and human handoff
Design a support assistant that people can access, understand and leave for human help without starting their request again.
Read the guide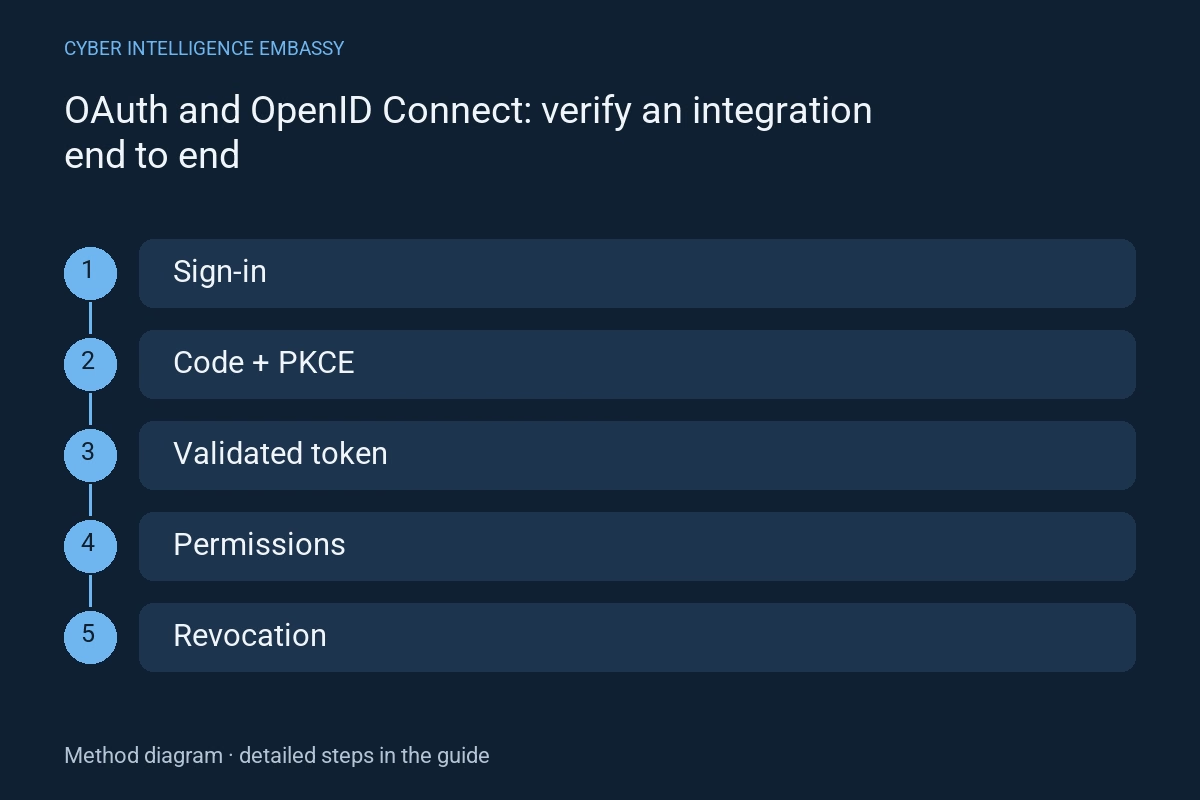
OAuth and OpenID Connect: verify an integration end to end
Separate sign-in, delegation and data permissions, then test redirects, tokens, sessions and revocation.
Read the guide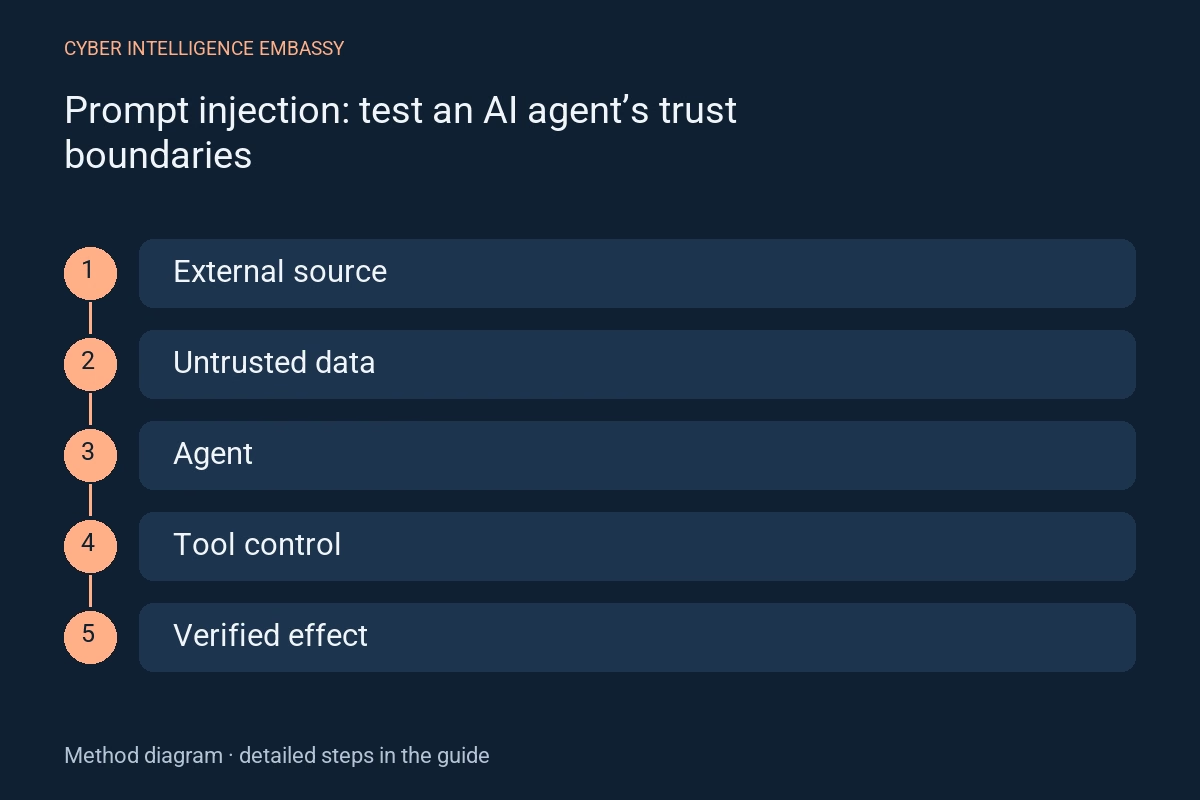
Prompt injection: test an AI agent’s trust boundaries
Check that a document, search result or message cannot authorise an action on behalf of the user.
Read the guide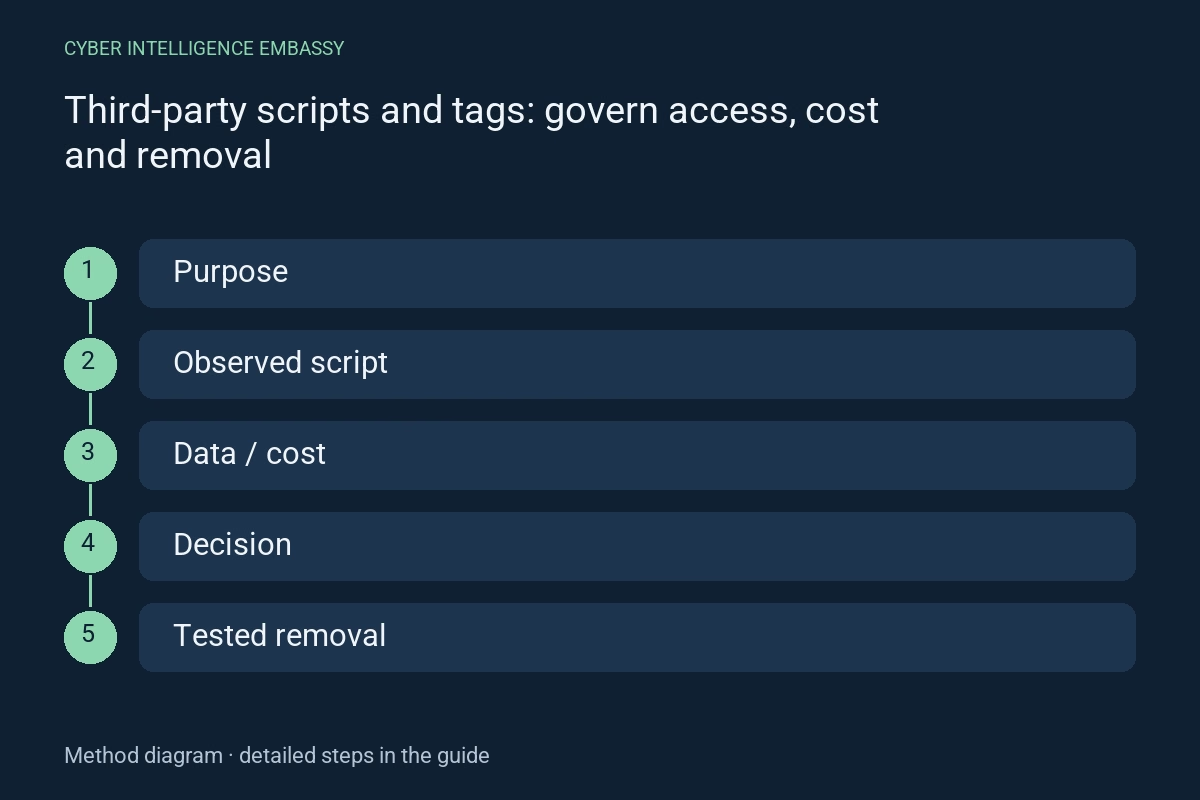
Third-party scripts and tags: govern access, cost and removal
Connect each script to a purpose, owner, visible data and a tested shutdown path.
Read the guide
Data reliability: diagnose a dashboard before making a decision
Separate a real decline from late data, broken collection and a changed definition.
Read the guide
Uncertain payments: recover checkout without duplicate orders
Reconcile network delays, browser returns, notifications and business state instead of treating any one signal as sufficient.
Read the guide
Editorial media: provenance, alternatives and useful integration
Choose between photographs, illustrations and diagrams, disclose their status and communicate beyond pixels.
Read the guide
Evaluate AI regressions before changing versions
Compare versions on the same tasks, find local losses and make a decision supported by cases rather than an average.
Read the guide
Small samples: communicate measurement uncertainty
Show counts, period and limitations before interpreting a rate or recommending action.
Read the guide
Campaign links and UTMs: keep measurement coherent
Connect published links to known campaigns, test redirects and interpret visits without claiming complete attribution.
Read the guide
Portability: verify an exit from a digital supplier
Test export, reconstruction and continuity before contractual or technical dependencies make an exit impractical.
Read the guide
Search and facets: make a catalog usable
Connect customer language, reliable attributes and filter states to clear results and controlled URLs.
Read the guide
Webhooks: handle repeats, delays and recovery
Turn a received notification into a unique, traceable business effect recoverable after failure.
Read the guide
URL migration: prepare SEO and user acceptance
Give every old address a relevant decision and verify destinations, signals and journeys before cutover.
Read the guide
Social accounts: prepare impersonation, access loss and recovery
Connect accounts to owners, permissions and a verified response available when the main channel is compromised.
Read the guide
Dialogs and keyboards: test the focus journey
Check opening, movement, closing and context restoration in interfaces that interrupt a task.
Read the guide
RAG: verify document access rights and isolation
Test retrieval, citations, caches and revocation so a document assistant respects each user’s permissions.
Read the guide
Retention cohorts: compare observable windows
Define entry, return and horizon, distinguish no return from an unobservable period and compare cohorts with completed observation windows.
Read the guide
Influencer campaigns: connect deliverables, evidence and measurement
Prepare a verifiable brief, inspect published content and distinguish attributed sales, margin and effects actually demonstrated.
Read the guide
Project acceptance: turn needs into criteria and evidence
Prepare scenarios, expected outcomes, evidence and exception decisions to assess a delivery through tasks actually tested.
Read the guide
Inventory: verify availability, reservations and concurrency
Distinguish physical, sellable, reserved and incoming stock, then test concurrent purchases, cancellations and channel synchronisation.
Read the guide
HTTP caching: protect personalized responses
Separate shared, private and application caches, inspect keys, revalidation and invalidation after access-right changes.
Read the guide
Structured data: verify meaning, evidence and supported features
Connect JSON-LD to visible content, separate vocabulary validity from Google support and review templates and exceptions after changes.
Read the guide
Social video: prepare captions, transcripts and alternatives
Plan useful information before editing, review captions and check that sound, visuals, cropping and translation preserve meaning.
Read the guide
Animation: verify reduced motion, pause and understanding
Inventory motion, offer reduced behaviour and test that progress, state and navigation remain understandable without animation.
Read the guide
AI agents: authorize an action and verify its effect
Bind human approval to a specific operation, limit its lifetime and account for effects already executed.
Read the guide
Data joins: avoid multiplying business metrics
Verify grain, keys and cardinality before totaling sales, costs or conversions.
Read the guide
Advertising: distinguish attribution from incrementality
Understand what reports attribute and what a protocol can estimate as an additional effect.
Read the guide
Digital services: compare total cost and cost per outcome
Include migration, operation, quality, support and exit in an explicit comparison.
Read the guide
Returns and refunds: connect customer cases to payment state
Separate return approval, receipt, requested refunds and confirmed outcomes.
Read the guide
URL imports: prevent unauthorized server requests
Prevent SSRF in downloads, previews and connectors accessing user-supplied addresses.
Read the guide
JavaScript SEO: check received and rendered content
Compare HTTP responses, rendering and interactions to find information missing during crawling.
Read the guide
Social content: prepare a usable and proportionate archive
Retain necessary context, versions and media and test what an export actually reconstructs.
Read the guide
Network failures: preserve input and resume a task
Describe waiting, failure and uncertain outcomes without losing the person’s work.
Read the guide
Published numbers: verify sources, calculations and interpretation
An editorial review procedure separating documented statistics, fictional examples, targets and commercial promises.
Read the guide
API quotas: bound load and recover without a retry storm
Define budgets, counting identities and recovery behavior when a client reaches a limit.
Read the guide
Data tables: preserve meaning on mobile and with screen readers
Structure units, headers, sorting and alternatives so comparisons remain usable.
Read the guide
Software carbon impact: define boundaries before comparing
Separate transferred volume, energy, emissions and delivered service to avoid unverified environmental gains.
Read the guide
AI search: verify visibility and publication controls
Separate crawling, indexing, previews and AI service usage before changing site directives.
Read the guide
AI extraction: validate JSON before integration
Separate parsing, schema checks, documentary evidence and business rules when turning documents into usable records.
Read the guide
Reliable reports: time zones, cutoffs and late events
Avoid shifted reporting days, duplicate counts and inconsistent comparisons between exports and dashboards.
Read the guide
Email marketing: preferences and unsubscribe choices that take effect
Connect links, headers, CRM records and sending queues so preference changes reach every campaign.
Read the guide
Architecture decisions: retain the rationale and know when to reconsider
Document consequential choices without turning every meeting into an oversized dossier.
Read the guide
Customer reviews: provenance, moderation and consistent ratings
Explain verified-review labels and keep moderation fair from submission to structured data.
Read the guide
API pagination: complete exports without missing or duplicated records
Define ordering, tokens, authorization and recovery when a collection changes during traversal.
Read the guide
Paginated lists: make catalogs accessible and crawlable
Coordinate URLs, links and incremental loading so items deeper in a collection remain discoverable.
Read the guide
Social platforms: compare metrics without false equivalence
Build a metric dictionary before comparing platforms, formats and campaigns.
Read the guide
Accessible status messages: confirm actions without losing context
Make search results, saves, progress and errors perceptible visually, by keyboard and with screen readers.
Read the guide
Synthetic data: verify privacy and task utility
Evaluate generated records before sharing them or using them to train a model.
Read the guide
Means and percentiles: aggregate without hiding slow tasks
Compare performance using consistent populations, units and time windows.
Read the guide
CRM leads: qualify with criteria and evidence
Connect acquisition, contact quality and handover to sales.
Read the guide
Software inventory: prepare for end of support
Turn a tool list into maintenance, replacement and retirement decisions.
Read the guide
Commerce: verify currency amounts and rounding
Reconcile displayed prices, orders, payments and refunds without mixing units.
Read the guide
File uploads: validate before processing or publishing
Control format, resources, access and states from receipt to download.
Read the guide
HTTP status and soft 404: diagnose before fixing
Connect server responses, visible content and indexing decisions.
Read the guide
Social images: write alternatives that preserve meaning
Make photos, carousels, charts and creative assets understandable beyond pixels.
Read the guide
Responsive images: test srcset, sizes and cropping
Deliver an appropriate variant without losing the subject, readability or layout stability.
Read the guide
Shared caching: test privacy, variants and invalidation
Speed up public responses while preventing cross-account reuse and checking how outdated versions are removed.
Read the guide
URL migration: prepare mappings and test redirects
Change domain or URL structure while preserving useful destinations for old pages and their language editions.
Read the guide
Progressive releases: stop criteria and rollback
Expand a new version using comparable observations and an exercised recovery path.
Read the guide
OCR: validate document reading before automation
Check omissions, numbers and reading order before transcription feeds search or decisions.
Read the guide
Missing data: distinguish absence, zero and estimation
Prevent silent replacement of absent values from changing the meaning of metrics.
Read the guide
Campaign QR codes: verify the printed material and destination
Test the path from print to digital service, including redirects and campaign retirement.
Read the guide
Retiring a digital service: remaining needs, data and handover
Organise closure without abandoning ongoing cases, users or retention responsibilities.
Read the guide
Subscriptions: connect cancellation, billing and access rights
Verify what changes after a stop request, immediately or at a planned period boundary.
Read the guide
Asynchronous API jobs: track status, resume and cancel
Separate accepted requests, started processing and final outcomes of long-running operations.
Read the guide
Sitemaps: verify URLs, shards and lastmod dates
Check the file offered to crawlers beyond simple XML syntax validity.
Read the guide
Community polls: interpret who responds and who is missing
Use answers as a documented signal without automatically treating them as the opinion of an entire audience.
Read the guide
Localized input: resolve number and date ambiguity
Accept and confirm values without silently changing separators, units or date order.
Read the guide
Passkeys: prepare a domain and RP ID change
Separate business account, web origin and RP ID to plan a transition without silently rebinding credentials.
Read the guide
Software updates: verify a signer identity change
Decide whether a signed artifact still matches the approved producer, build process and release.
Read the guide
Collection outages: reconcile logs and missing events
Separate produced, received and usable events to explain an outage without treating silence as absence of incidents.
Read the guide
AI citations: check an answer when its source changes
Bind claims to a document version and passage, then handle stale citations without rewriting history.
Read the guide
Dangling subdomains: retire a CNAME without leaving a claimable dependency
Tie each DNS name to a controlled resource and make DNS cleanup part of service retirement.
Read the guide
postMessage: verify origin, window and requested command
Define an iframe or popup messaging contract that rejects unexpected senders, payloads and operation states.
Read the guide
ZIP and TAR archives: extract within a directory and resource budget
Validate paths, links and expanded data before promoting files from an archive.
Read the guide
TLS renewal: verify the certificate actually being served
Follow renewal through every termination point and supported client before declaring the change complete.
Read the guideOperational data
Digital maturity matrix — 315 verifiable controls
An open framework to assess the existence, application, evidence and management of essential controls. It is not a certification: it makes gaps easier to discuss and prioritise.
Assessment scale
No stable practice or usable evidence.
Occasional practice dependent on one person.
Documented, applied and verifiable control.
Measured, reviewed and improved control.
Prepare your assessment
Set the scope, then assess relevant controls. Not assessed, absent and not applicable remain distinct. Notes stay in this tab; export them before closing it. No results are sent to the server.
Assessment overview
- Not assessed
- 0
- 0 — Absent
- 0
- 1 — Initial
- 0
- 2 — Controlled
- 0
- 3 — Managed
- 0
- Not applicable
- 0
- Recorded actions
- 0
The CSV includes only controls with a next action. Unknown scores stay empty; no overall score is calculated.
Levels 2 and 3 need an evidence reference; exclusions need a rationale. The result is not a certification.
| Domain | Verifiable control | Minimum expected evidence | Your assessment |
|---|---|---|---|
| OSINT | Decision question defined before collectionCIE-0001 · Method and references | Dated brief with scope, audience and expected decision | Not assessed |
| OSINT | Sources classified by origin, date and reliabilityCIE-0002 · Method and references | Source log and explicit scoring rule | Not assessed |
| OSINT | Facts, hypotheses and unknowns kept separateCIE-0003 · Method and references | Analysis note with confidence levels | Not assessed |
| OSINT | Sensitive information minimised and protectedCIE-0004 · Method and references | Retention rule and access register | Not assessed |
| Cybersecurity | Inventory of exposed assets maintainedCIE-0005 · Method and references | List of domains, services, accounts and owners | Not assessed |
| Cybersecurity | Critical access protected by resistant MFACIE-0006 · Method and references | Coverage report and approved exceptions | Not assessed |
| Cybersecurity | Patches prioritised by exposure and impactCIE-0007 · Method and references | Dated remediation queue and closure evidence | Not assessed |
| Cybersecurity | Backups restored during a testCIE-0008 · Method and references | Report from the latest restoration test | Not assessed |
| AI agents | Agent purpose, limits and owner documentedCIE-0009 · Method and references | System card and responsibility matrix | Not assessed |
| AI agents | Allowed and prohibited data identifiedCIE-0010 · Method and references | Data classification and applied filters | Not assessed |
| AI agents | Sensitive answers evaluated on a test setCIE-0011 · Method and references | Results, acceptance thresholds and known errors | Not assessed |
| AI agents | Logging and manual stop availableCIE-0012 · Method and references | Execution logs and shutdown procedure | Not assessed |
| Visibility | Search intents connected to useful pagesCIE-0013 · Method and references | Intent, page, action and metric map | Not assessed |
| Visibility | Entities, authors and dates are explicitCIE-0014 · Method and references | Consistent visible markup and structured data | Not assessed |
| Visibility | Mobile journeys and performance controlledCIE-0015 · Method and references | Field measurements and key action tests | Not assessed |
| Visibility | Conversions connected to entry contentCIE-0016 · Method and references | Dashboard by page and business objective | Not assessed |
| Digital trust | Identity, beneficial ownership and governance verifiedCIE-0017 · Method and references | Dated source file with unresolved points clearly marked | Not assessed |
| Digital trust | Critical dependencies and subcontractors mappedCIE-0018 · Method and references | Third-party map covering services, data and fallback options | Not assessed |
| Digital trust | Incidents, disputes and reputation signals qualifiedCIE-0019 · Method and references | Sourced timeline separating facts, allegations and responses | Not assessed |
| Digital trust | Decision documented with conditions and monitoringCIE-0020 · Method and references | Decision note, reservations, owner and review triggers | Not assessed |
| Secure web | Performance budget defined for critical journeysCIE-0021 · Method and references | Mobile thresholds for loading, interaction and visual stability | Not assessed |
| Secure web | Dependencies and third-party scripts minimisedCIE-0022 · Method and references | Inventory, rationale, owner and removal procedure | Not assessed |
| Secure web | Headers, sessions and forms hardenedCIE-0023 · Method and references | Control report and server-side protection tests | Not assessed |
| Secure web | Accessibility and key actions tested in real useCIE-0024 · Method and references | Documented keyboard, screen reader, mobile and error scenarios | Not assessed |
| Third-party risk | Critical suppliers classified by service, data and dependencyCIE-0025 · Method and references | Supplier register with owner, criticality and fallback option | Not assessed |
| Third-party risk | Contractual and operational evidence verifiedCIE-0026 · Method and references | Dated file covering security, continuity, subcontractors and data location | Not assessed |
| Third-party risk | Concentration and dependency chains analysedCIE-0027 · Method and references | Map of critical subcontractors and failure scenarios | Not assessed |
| Third-party risk | Exit and reversibility conditions testedCIE-0028 · Method and references | Exit procedure, controlled export and replacement exercise | Not assessed |
| Crisis management | Decision roles and fallback channels definedCIE-0029 · Method and references | Offline crisis directory and responsibility matrix | Not assessed |
| Crisis management | Incident scenarios exercised with business teamsCIE-0030 · Method and references | Exercise report, observed decisions and gaps | Not assessed |
| Crisis management | Recovery prioritised by essential serviceCIE-0031 · Method and references | Approved recovery order and technical test evidence | Not assessed |
| Crisis management | Internal and external communication preparedCIE-0032 · Method and references | Adaptable templates, notification criteria and named spokesperson | Not assessed |
| RAG quality | Corpus, rights and validity dates controlledCIE-0033 · Method and references | Source inventory, owner, update cycle and exclusions | Not assessed |
| RAG quality | Retrieval evaluated separately from generationCIE-0034 · Method and references | Question set measuring passage relevance and coverage | Not assessed |
| RAG quality | Citations traced back to sourceCIE-0035 · Method and references | Faithfulness tests, valid links and unsupported-claim rate | Not assessed |
| RAG quality | Failures and abstentions monitored in productionCIE-0036 · Method and references | Edge-case log, escalation thresholds and drift review | Not assessed |
| Information integrity | Provenance and original context retainedCIE-0037 · Method and references | Verification log with file, source, date and transformations | Not assessed |
| Information integrity | Images and video corroborated with independent cluesCIE-0038 · Method and references | Geolocation, chronology and earlier-version record | Not assessed |
| Information integrity | Confidence and unknowns explicit before publicationCIE-0039 · Method and references | Editorial decision with confidence level and caveats | Not assessed |
| Information integrity | Corrections propagated to dependent contentCIE-0040 · Method and references | Correction register, linked pages and reverification date | Not assessed |
| Identity | Account lifecycle connected to HR and business eventsCIE-0041 · Method and references | Dated creation, change, suspension and deletion log with an owner | Not assessed |
| Identity | Account recovery protected against social engineeringCIE-0042 · Method and references | Verified procedure, independent factors, delays and escalation cases | Not assessed |
| Identity | Elevated privileges limited, temporary and reviewedCIE-0043 · Method and references | Role inventory, approvals, duration and latest access review | Not assessed |
| Identity | Lost-device and lockout scenarios exercisedCIE-0044 · Method and references | Test report covering revocation, recovery and continuity | Not assessed |
| Multilingual SEO | Each language edition has a stable canonical URLCIE-0045 · Method and references | Language, URL, canonical, status and editorial-owner map | Not assessed |
| Multilingual SEO | Language alternates are reciprocal and validCIE-0046 · Method and references | Hreflang check covering return links, codes, indexable URLs and x-default | Not assessed |
| Multilingual SEO | Translations adapted to intent and marketCIE-0047 · Method and references | Local brief, terminology validation and edition-specific examples | Not assessed |
| Multilingual SEO | Indexing, performance and conversion tracked by editionCIE-0048 · Method and references | Dashboard separating language, device, landing page and objective | Not assessed |
| Data lifecycle | Purpose, owner and retention period defined at collectionCIE-0049 · Method and references | Register linking category, use, owner, retention basis and deadline | Not assessed |
| Data lifecycle | Copies, backups and archives included in lifecycle rulesCIE-0050 · Method and references | Location, replication, restoration and propagation-delay map | Not assessed |
| Data lifecycle | Legal holds and retention exceptions are traceableCIE-0051 · Method and references | Dated decision, scope, authority, duration and release procedure | Not assessed |
| Data lifecycle | Deletion is verified and repeatableCIE-0052 · Method and references | Purge log, control sample and failed-deletion handling | Not assessed |
| AI vendors | Use, data and decision level framed before selectionCIE-0053 · Method and references | Need statement, prohibited cases, owner and exit criteria | Not assessed |
| AI vendors | Quality and limitations tested on representative casesCIE-0054 · Method and references | Versioned evaluation set, results, thresholds and known failures | Not assessed |
| AI vendors | Dependencies, subprocessors and changes monitoredCIE-0055 · Method and references | Technical map, contractual notifications and version log | Not assessed |
| AI vendors | Reversibility and data recovery exercisedCIE-0056 · Method and references | Tested export, replacement procedure, timelines and deletion evidence | Not assessed |
| AI visibility | Generative search report tracked by page and periodCIE-0057 · Method and references | Dated Search Console export with pages, impressions and scope | Not assessed |
| AI visibility | Sampled answers and citations manually verifiedCIE-0058 · Method and references | Query protocol, date, country, device and cited links | Not assessed |
| AI visibility | Changes connected to identifiable editorial workCIE-0059 · Method and references | Change log and before-after comparison without assumed causation | Not assessed |
| AI visibility | Traffic and business outcomes compared with visibilityCIE-0060 · Method and references | Dashboard connecting pages, qualified visits and conversions | Not assessed |
| Software supply chain | Direct and transitive components inventoried per releaseCIE-0061 · Method and references | Dated software bill of materials linked to the shipped version | Not assessed |
| Software supply chain | Artifact origin and integrity verifiableCIE-0062 · Method and references | Provenance, digest and signature check for shipped releases | Not assessed |
| Software supply chain | Vulnerabilities qualified by exposure and actual useCIE-0063 · Method and references | Triage queue with component, scope, owner, decision and evidence | Not assessed |
| Software supply chain | Critical component update and removal rehearsedCIE-0064 · Method and references | Replacement, test, deployment and rollback report | Not assessed |
| Domains and DNS | Critical domains and subdomains inventoried with ownersCIE-0065 · Method and references | Dated register of holder, registrar, expiry, DNS and accountable owner | Not assessed |
| Domains and DNS | Registrar access protected and changes approvedCIE-0066 · Method and references | Account review, strong authentication and change log | Not assessed |
| Domains and DNS | Delegation and DNSSEC checked after changeCIE-0067 · Method and references | Resolution and validation results from multiple networks | Not assessed |
| Domains and DNS | DNS recovery rehearsed with out-of-band contactsCIE-0068 · Method and references | Exercise report, recovery time and corrective actions | Not assessed |
| API resilience | Critical dependencies mapped to business journeysCIE-0069 · Method and references | Call map, owners, contracts and degraded modes | Not assessed |
| API resilience | Timeouts, retries and idempotency testedCIE-0070 · Method and references | Timeout, backoff and idempotency-key test results | Not assessed |
| API resilience | Controlled degradation exercised during simulated outageCIE-0071 · Method and references | Failure scenario and evidence of user-facing behaviour | Not assessed |
| API resilience | Alerts linked to business impact and recoveryCIE-0072 · Method and references | Dashboard, thresholds, on-call owner and restoration report | Not assessed |
| Browser extensions | Installed extensions and owners inventoriedCIE-0073 · Method and references | Dated inventory by browser, version, team and accountable owner | Not assessed |
| Browser extensions | Permissions and site access justifiedCIE-0074 · Method and references | Review of manifest, allowed hosts and accessible data | Not assessed |
| Browser extensions | Installation and updates controlledCIE-0075 · Method and references | Deployment policy, approved list and change review | Not assessed |
| Browser extensions | Removal and incidents rehearsedCIE-0076 · Method and references | Disablement procedure, scope and removal evidence | Not assessed |
| Backup and recovery | Critical services and dependencies prioritisedCIE-0077 · Method and references | Impact analysis, recovery order and accountable owners | Not assessed |
| Backup and recovery | Protected and isolated copies verifiedCIE-0078 · Method and references | Copy inventory, access rights and availability evidence | Not assessed |
| Backup and recovery | Restoration rehearsed safelyCIE-0079 · Method and references | Timestamped test report, functional outcome and observed gaps | Not assessed |
| Backup and recovery | Recovery objectives compared with realityCIE-0080 · Method and references | Observed recovery time and data loss during the exercise | Not assessed |
| Incident triage | Reporting channel and decision owner definedCIE-0081 · Method and references | Escalation procedure, deputy and decision log | Not assessed |
| Incident triage | Initial timeline and evidence preservedCIE-0082 · Method and references | Dated events, sources, integrity and access recorded | Not assessed |
| Incident triage | Impact and scope reassessedCIE-0083 · Method and references | Hypotheses, affected services, decisions and next checkpoints | Not assessed |
| Incident triage | Lessons turned into actionsCIE-0084 · Method and references | Actions, owners, dates and closure validation | Not assessed |
| Web accessibility | Scope and reference level definedCIE-0085 · Method and references | Journeys, languages, components and selected WCAG criteria | Not assessed |
| Web accessibility | Representative sample examinedCIE-0086 · Method and references | Page types, interactive states and essential content covered | Not assessed |
| Web accessibility | Automated and manual tests combinedCIE-0087 · Method and references | Keyboard, zoom, screen reader and human review evidence | Not assessed |
| Web accessibility | Fixes retested across the journeyCIE-0088 · Method and references | Reproducible finding, owner, retest and user effect | Not assessed |
| Vulnerability management | Assets and versions assigned to ownersCIE-0089 · Method and references | Dated register of services, components and owners | Not assessed |
| Vulnerability management | Known exploitation checkedCIE-0090 · Method and references | CVE, CISA KEV listing and actually deployed product matched | Not assessed |
| Vulnerability management | Priority reflects exposure and impactCIE-0091 · Method and references | Dated decision with business risk, deadline and compensating measures | Not assessed |
| Vulnerability management | Fix and functionality verifiedCIE-0092 · Method and references | Deployed version, vulnerability check and critical journey test | Not assessed |
| Phishing-resistant authentication | Accounts and current methods inventoriedCIE-0093 · Method and references | Users, privileges, factors and applications recorded | Not assessed |
| Phishing-resistant authentication | Binding to genuine service checkedCIE-0094 · Method and references | Legitimate-domain test and phishing scenario rejection | Not assessed |
| Phishing-resistant authentication | Enrollment and fallback protectedCIE-0095 · Method and references | Addition, loss, revocation and notification procedure tested | Not assessed |
| Phishing-resistant authentication | Migration and exceptions trackedCIE-0096 · Method and references | Coverage, excluded accounts, owners and closure dates | Not assessed |
| Measurement plan | Objective and event linkedCIE-0097 · Method and references | Dictionary with journey, event, owner and decision | Not assessed |
| Measurement plan | Parameters and types documentedCIE-0098 · Method and references | Names, types, units and collection rules approved | Not assessed |
| Measurement plan | Events tested across statesCIE-0099 · Method and references | Consent, duplicate, error, mobile and abandonment tests | Not assessed |
| Measurement plan | Quality monitored after releaseCIE-0100 · Method and references | Expected versus received events with an assigned owner | Not assessed |
| Experimentation | Hypothesis and population preregisteredCIE-0101 · Method and references | Dated protocol, primary metric and excluded segments | Not assessed |
| Experimentation | Assignment checkedCIE-0102 · Method and references | Allocation and observed sample ratio examined | Not assessed |
| Experimentation | Operational guardrails monitoredCIE-0103 · Method and references | Errors, latency, accessibility and checkout tracked | Not assessed |
| Experimentation | Decision and uncertainty documentedCIE-0104 · Method and references | Result, duration, limits, segments and next action archived | Not assessed |
| Measurement and privacy | Trackers and purposes inventoriedCIE-0105 · Method and references | Map of access, recipients, retention and purposes | Not assessed |
| Measurement and privacy | Configuration assessed against applicable rulesCIE-0106 · Method and references | Documented CNIL conditions and consent choices | Not assessed |
| Measurement and privacy | Refusal tested end to endCIE-0107 · Method and references | Evidence before choice, after refusal and withdrawal | Not assessed |
| Measurement and privacy | Access and retention reviewedCIE-0108 · Method and references | Permissions, periods and periodic review register | Not assessed |
| Product catalog | Stable identifier per offerCIE-0109 · Method and references | Verifiable link across item, variant, URL and feed | Not assessed |
| Product catalog | Price and availability consistentCIE-0110 · Method and references | Timestamped feed, visible page and structured data check | Not assessed |
| Product catalog | Variants and images checkedCIE-0111 · Method and references | Sample of sizes, colors, visuals and descriptions | Not assessed |
| Product catalog | Discrepancies owned and fixedCIE-0112 · Method and references | Discrepancy log, owner, fix and recheck | Not assessed |
| Security logging | Critical sources and clocks inventoriedCIE-0113 · Method and references | Systems, events, time sync and owner inventory | Not assessed |
| Security logging | Log integrity and access protectedCIE-0114 · Method and references | Transfer, retention, permission and tamper checks | Not assessed |
| Security logging | Correlation tested with a scenarioCIE-0115 · Method and references | Identifiers connecting sign-in, application and infrastructure | Not assessed |
| Security logging | Detection linked to responseCIE-0116 · Method and references | Tested rule, owner, timing and response evidence | Not assessed |
| Multilingual quality | Languages and canonical versions mappedCIE-0117 · Method and references | URL, HTML language and reciprocal alternate inventory | Not assessed |
| Multilingual quality | Journeys translated end to endCIE-0118 · Method and references | Navigation, form, error, email and checkout tests | Not assessed |
| Multilingual quality | Direction and formats testedCIE-0119 · Method and references | RTL, date, number, unit and overflow checks | Not assessed |
| Multilingual quality | Review and fixes recordedCIE-0120 · Method and references | Human sample, risk level, owner and retest | Not assessed |
| Crawling and indexing | Important URLs discoverableCIE-0121 · Method and references | HTML links and sitemap reach accessible canonical URLs | Not assessed |
| Crawling and indexing | Responses and directives coherentCIE-0122 · Method and references | HTTP, robots, noindex and canonical sample checked | Not assessed |
| Crawling and indexing | Search Console gaps diagnosedCIE-0123 · Method and references | URL inspection, logs and documented cause before fix | Not assessed |
| Crawling and indexing | Fixes retestedCIE-0124 · Method and references | Links, responses, tags and pages rechecked after release | Not assessed |
| Accessible forms | Fields named and groupedCIE-0125 · Method and references | Labels, groups, help and keyboard order checked | Not assessed |
| Accessible forms | Errors locatable and correctableCIE-0126 · Method and references | Summary, field message and retained values tested | Not assessed |
| Accessible forms | Complete states verifiedCIE-0127 · Method and references | Success, server failure, delay, mobile and zoom rehearsed | Not assessed |
| Accessible forms | Journey tested with assistanceCIE-0128 · Method and references | Keyboard and relevant assistive technology on a real task | Not assessed |
| API contracts | Requests and responses documentedCIE-0129 · Method and references | OpenAPI description with examples, schemas and statuses | Not assessed |
| API contracts | Errors actionable without leakageCIE-0130 · Method and references | Type, status and useful detail validated without secrets | Not assessed |
| API contracts | Compatibility exercisedCIE-0131 · Method and references | Old clients, optional fields and new versions tested | Not assessed |
| API contracts | Webhooks replay-safeCIE-0132 · Method and references | Signature, duplicate, ordering, retry and acknowledgement tested | Not assessed |
| Email delivery | Sender authentication checkedCIE-0133 · Method and references | SPF, DKIM, DMARC and alignment inspected on real messages | Not assessed |
| Email delivery | Message classes separatedCIE-0134 · Method and references | Promotional and transactional flows and measures distinguished | Not assessed |
| Email delivery | Promotional unsubscribe testedCIE-0135 · Method and references | Visible link and applicable one-click headers verified | Not assessed |
| Email delivery | Rejections and complaints monitoredCIE-0136 · Method and references | Bounces, reputation and failure causes documented | Not assessed |
| Editorial maintenance | Page tied to need and ownerCIE-0137 · Method and references | Purpose, audience, source and owner recorded | Not assessed |
| Editorial maintenance | Review date and triggers setCIE-0138 · Method and references | Deadline and changes in facts, service or policy tracked | Not assessed |
| Editorial maintenance | Lifecycle decision documentedCIE-0139 · Method and references | Keep, correct, merge or retire with reason | Not assessed |
| Editorial maintenance | Removal and links checkedCIE-0140 · Method and references | Redirects, internal references and language versions retested | Not assessed |
| Community moderation | Rules visible and actionableCIE-0141 · Method and references | Prohibited behaviors, actions and appeal path published | Not assessed |
| Community moderation | Priorities and escalation definedCIE-0142 · Method and references | Urgency, owner, channel and timing by scenario | Not assessed |
| Community moderation | Sensitive decisions reviewedCIE-0143 · Method and references | Removal, blocking, reporting and responses recorded | Not assessed |
| Community moderation | Scenarios rehearsedCIE-0144 · Method and references | Complaint, threat and moderation-error exercise with correction | Not assessed |
| Real-world performance | Slow interactions grouped by journey and componentCIE-0145 · Method and references | Segmented INP data and a reproduction scenario on an affected device | Not assessed |
| Real-world performance | Unexpected visual shifts checked in late statesCIE-0146 · Method and references | CLS sample covering media, advertising and error loading | Not assessed |
| Real-world performance | Cache tested for a sensitive changeCIE-0147 · Method and references | Price, stock, permission or publication test with measured propagation delay | Not assessed |
| Real-world performance | Server wait separated from browser renderingCIE-0148 · Method and references | TTFB, cache, request and rendering timeline for priority pages | Not assessed |
| Interface security | Access to each object enforced by the serviceCIE-0149 · Method and references | Read and write tests using an object belonging to another account | Not assessed |
| Interface security | Old API versions inventoried before retirementCIE-0150 · Method and references | Consumer list, migration deadline and remaining traffic | Not assessed |
| Interface security | Retries bounded during dependency failureCIE-0151 · Method and references | Test of attempt count, timing, load and final failure | Not assessed |
| Interface security | Signed webhooks checked against replayCIE-0152 · Method and references | Tests with invalid signature, old timestamp and already processed identity | Not assessed |
| AI answer quality | Unanswerable questions included in evaluationCIE-0153 · Method and references | Documented cases and abstention rate checked after corpus changes | Not assessed |
| AI answer quality | Retrieval and answer faithfulness measured separatelyCIE-0154 · Method and references | Document relevance judgments and review of generated claims | Not assessed |
| AI answer quality | Model and corpus changes replayed on the same casesCIE-0155 · Method and references | Comparable results by version and investigation of regressions | Not assessed |
| AI answer quality | Agent tools restricted by actionCIE-0156 · Method and references | Allowlist, permissions, approvals and denials tested for every tool | Not assessed |
| Catalog reliability | Stock update delay measured by channelCIE-0157 · Method and references | Timestamps compared across source, product page, cart and external feed | Not assessed |
| Catalog reliability | Variant selection updates every attributeCIE-0158 · Method and references | Tests of images, price, dimensions, availability and structured offer | Not assessed |
| Catalog reliability | Stockout and promotion exercised through checkoutCIE-0159 · Method and references | Dated scenarios showing consistent display, selection and final result | Not assessed |
| Catalog reliability | Data correction propagated from its sourceCIE-0160 · Method and references | Catalog incident traced through corrected page, feed and markup | Not assessed |
| Journeys and delivery | Focus returns after error or dialog closureCIE-0161 · Method and references | Recorded keyboard journey showing focus position and task resumption | Not assessed |
| Journeys and delivery | Form constraints known before submissionCIE-0162 · Method and references | Test of help, accepted formats, validation and retained entries | Not assessed |
| Journeys and delivery | Permanent and temporary email bounces separatedCIE-0163 · Method and references | Sample of codes, causes and retry or removal decisions | Not assessed |
| Journeys and delivery | URL migration checked from old linksCIE-0164 · Method and references | Redirect map, final responses, canonical and internal links retested | Not assessed |
| GraphQL security | Object and field permissions testedCIE-0165 · Method and references | Allowed and denied cases for each role on cross-owned objects | Not assessed |
| GraphQL security | Query cost boundedCIE-0166 · Method and references | Depth, breadth, pagination and aliases checked on real queries | Not assessed |
| GraphQL security | Errors and introspection configuredCIE-0167 · Method and references | Public responses avoid sensitive detail; schema exposure decided | Not assessed |
| GraphQL security | Abuse and denials observableCIE-0168 · Method and references | Load and permission tests correlated with privacy-aware logs | Not assessed |
| Product variants | Each variant has stable identityCIE-0169 · Method and references | Identifier, distinguishing attributes and group checked in page and markup | Not assessed |
| Product variants | URL selects the intended variantCIE-0170 · Method and references | Direct link tested with matching image, price, stock and cart action | Not assessed |
| Product variants | Price and stock sources synchronizedCIE-0171 · Method and references | Discrepancies and delay measured across catalog, page, cart and feed | Not assessed |
| Product variants | Stockouts and changes replayedCIE-0172 · Method and references | Unavailable variants, promotions and substitutions tested without phantom offers | Not assessed |
| Field web metrics | Field data segmentedCIE-0173 · Method and references | URL or group, device, period and population defined before comparison | Not assessed |
| Field web metrics | INP tied to an interactionCIE-0174 · Method and references | Slow actions reproduced with trace and responsible component | Not assessed |
| Field web metrics | LCP and CLS attributed to elementsCIE-0175 · Method and references | Largest element and unexpected shifts located on representative pages | Not assessed |
| Field web metrics | Fix tracked in field and labCIE-0176 · Method and references | Same journey and segments measured before and after with documented limits | Not assessed |
| Social listening | Collection scope recordedCIE-0177 · Method and references | Sources, terms, languages, period and coverage gaps documented | Not assessed |
| Social listening | Signal deduplicated and contextualizedCIE-0178 · Method and references | Original post, copies, apparent author and date separated | Not assessed |
| Social listening | Facts separated from interpretationCIE-0179 · Method and references | Independent sources, contrary evidence and confidence recorded | Not assessed |
| Social listening | Urgent cases routed and closedCIE-0180 · Method and references | Severity, owner, response time, action and review tracked | Not assessed |
| OAuth and OIDC | Code flow and PKCE checked in deployed configurationCIE-0181 · Method and references | Verifier, replayed-code and unregistered-redirect tests | Not assessed |
| OAuth and OIDC | Token audience and issuer checkedCIE-0182 · Method and references | Rejection of valid tokens meant for another service or provider | Not assessed |
| OAuth and OIDC | Business permissions tested by object and operationCIE-0183 · Method and references | Cross-account and cross-role cases with denial results | Not assessed |
| OAuth and OIDC | Revocation exercised across sessions and tokensCIE-0184 · Method and references | Access-removal timeline after departure or role change | Not assessed |
| Prompt injection | Untrusted inputs and tools mappedCIE-0185 · Method and references | Channels, sources, tools and trust-boundary inventory | Not assessed |
| Prompt injection | Forbidden effects denied outside the modelCIE-0186 · Method and references | Permission and argument tests confirming absence of effects | Not assessed |
| Prompt injection | Adversarial cases isolated from real accessCIE-0187 · Method and references | Simulated environment with markers and recorded versions | Not assessed |
| Prompt injection | Regressions and false refusals trackedCIE-0188 · Method and references | Results replayed after model, source or tool changes | Not assessed |
| Third-party scripts | Loading chain observed by journeyCIE-0189 · Method and references | Initial and downstream requests by device and collection choice | Not assessed |
| Third-party scripts | Tags connected to purpose and approvalCIE-0190 · Method and references | Register with owner, usefulness and publishing permissions | Not assessed |
| Third-party scripts | Data access and cost verifiedCIE-0191 · Method and references | Observed flows and journey comparison with and without the script | Not assessed |
| Third-party scripts | Removal and provider outage testedCIE-0192 · Method and references | Working journey with no remaining indirect loading | Not assessed |
| Data reliability | Metric contract and lineage availableCIE-0193 · Method and references | Definition, unit, time zone, source, transformations and history | Not assessed |
| Data reliability | Freshness and completeness measured separatelyCIE-0194 · Method and references | Latest processed event and reconciliation of expected items | Not assessed |
| Data reliability | Values reconciled on known casesCIE-0195 · Method and references | Source-to-output sample with filter and join rules | Not assessed |
| Data reliability | Replay and partial status explicitly handledCIE-0196 · Method and references | Duplicate-free correction and visible chart quality status | Not assessed |
| Payment recovery | Payment and order states separatedCIE-0197 · Method and references | Transitions and authoritative source documented by payment method | Not assessed |
| Payment recovery | Uncertain response checked before another chargeCIE-0198 · Method and references | Timeout test checking the existing operation | Not assessed |
| Payment recovery | Notifications verified and deduplicatedCIE-0199 · Method and references | Signature, repeat and reversed-order tests without duplicate fulfilment | Not assessed |
| Payment recovery | Discrepancies reconciled with the providerCIE-0200 · Method and references | Uncertain-case queue with decision, owner and closure evidence | Not assessed |
| Editorial media | Media role and provenance documentedCIE-0201 · Method and references | Origin, status, use conditions and affected pages | Not assessed |
| Editorial media | Synthetic illustrations disclosed to readersCIE-0202 · Method and references | Visible distinction between fictional scenes and documentary evidence | Not assessed |
| Editorial media | Role-appropriate alternatives and explained diagramsCIE-0203 · Method and references | Role-based alt and textual description of complex relationships | Not assessed |
| Editorial media | Delivered variants checked on mobileCIE-0204 · Method and references | Dimensions, bytes, readability, crop and loading checked | Not assessed |
| AI regression | Reference set separate from optimisationCIE-0205 · Method and references | Provenance and versions of development and test sets | Not assessed |
| AI regression | Paired comparison retainedCIE-0206 · Method and references | Identical input, configurations and outcomes for both versions | Not assessed |
| AI regression | Sensitive losses separately reviewedCIE-0207 · Method and references | Segment outcomes and blocking-case adjudication | Not assessed |
| AI regression | Configuration rollback exercisedCIE-0208 · Method and references | Verified restoration of model, tools and sources | Not assessed |
| Measurement uncertainty | Rates accompanied by countsCIE-0209 · Method and references | Visible numerator, denominator and unit | Not assessed |
| Measurement uncertainty | Interval assumptions and method explicitCIE-0210 · Method and references | Confidence level, method and independence reviewed | Not assessed |
| Measurement uncertainty | Coverage and bias separate from precisionCIE-0211 · Method and references | Absent populations and collection limitations documented | Not assessed |
| Measurement uncertainty | Inconclusive conclusion permittedCIE-0212 · Method and references | Report without equating uncertainty to zero effect | Not assessed |
| Campaign links | Shared UTM convention across publishersCIE-0213 · Method and references | Dictionary and stable campaign identifier | Not assessed |
| Campaign links | Links checked after redirectsCIE-0214 · Method and references | Final URL and actually retained values | Not assessed |
| Campaign links | Personal data excluded from URLsCIE-0215 · Method and references | Review of published fields and parameters | Not assessed |
| Campaign links | Distribution and acquisition counters reconciledCIE-0216 · Method and references | Documented definitions, periods and discrepancies | Not assessed |
| Supplier portability | Task-based exit scope definedCIE-0217 · Method and references | Assets, essential functions and acceptable degradation | Not assessed |
| Supplier portability | Representative export verifiedCIE-0218 · Method and references | Relationships, metadata and attachments retrieved | Not assessed |
| Supplier portability | External reconstruction testedCIE-0219 · Method and references | Critical task completed in an isolated environment | Not assessed |
| Supplier portability | Effort and cutover documentedCIE-0220 · Method and references | Measured or estimated costs, order and rollback | Not assessed |
| Catalog search | Catalog query set reviewedCIE-0221 · Method and references | Intents, identifiers and expected results | Not assessed |
| Catalog search | Facet attributes normalisedCIE-0222 · Method and references | Coherent units, unknown values and variants | Not assessed |
| Catalog search | Filters and empty states accessibleCIE-0223 · Method and references | Removal, keyboard and back navigation tested | Not assessed |
| Catalog search | Facet crawling policy explicitCIE-0224 · Method and references | Useful combinations, status and canonical checked | Not assessed |
| Webhook processing | Authenticity verified before effectsCIE-0225 · Method and references | Signature and context denial tests with no actions | Not assessed |
| Webhook processing | Durable receipt before acknowledgmentCIE-0226 · Method and references | Queue failure test and receipt state | Not assessed |
| Webhook processing | Concurrent repeats without duplicate effectsCIE-0227 · Method and references | Business key and simultaneous-worker test | Not assessed |
| Webhook processing | Missing events reconciled and replayedCIE-0228 · Method and references | Error queue, source comparison and closure evidence | Not assessed |
| URL migration | Inventory includes media and filesCIE-0229 · Method and references | Discovery sources and scope limitations | Not assessed |
| URL migration | Justified mapping for every old URLCIE-0230 · Method and references | Relevant destination or explicit removal | Not assessed |
| URL migration | Redirects and signals alignedCIE-0231 · Method and references | Final status, links, canonical, hreflang and sitemap | Not assessed |
| URL migration | Cutover monitoring operationalCIE-0232 · Method and references | Errors, essential tasks and correction owner | Not assessed |
| Social accounts | Official accounts and owners inventoriedCIE-0233 · Method and references | URL, platform, owner and deputy | Not assessed |
| Social accounts | Access reviewed after departuresCIE-0234 · Method and references | Roles and integrations checked without copying secrets | Not assessed |
| Social accounts | Recovery simulated without real access lossCIE-0235 · Method and references | Procedure and contacts located by a deputy | Not assessed |
| Social accounts | Impersonation separated from compromiseCIE-0236 · Method and references | Facts, trusted channel and closure documented | Not assessed |
| Dialogs and keyboards | Named dialog and useful initial focusCIE-0237 · Method and references | Keyboard opening and announced heading | Not assessed |
| Dialogs and keyboards | Modal navigation and inert background verifiedCIE-0238 · Method and references | Tab, Shift+Tab and no outside interaction | Not assessed |
| Dialogs and keyboards | Closing and logical return exercisedCIE-0239 · Method and references | Escape, button and missing-trigger tests | Not assessed |
| Dialogs and keyboards | Long states and errors tested at zoomCIE-0240 · Method and references | Narrow-screen and assistive-technology acceptance | Not assessed |
| RAG access | Permissions enforced before model exposureCIE-0241 · Method and references | Server decision and unauthorised-group test | Not assessed |
| RAG access | Hybrid retrieval and citations coveredCIE-0242 · Method and references | Vector, lexical and direct-file tests | Not assessed |
| RAG access | Caches isolated by access contextCIE-0243 · Method and references | Same-question replay with two distinct scopes | Not assessed |
| RAG access | Revocation replayed on an existing conversationCIE-0244 · Method and references | Access-removal trace and refusal after invalidation | Not assessed |
| Observable cohorts | Inclusion and return specified separatelyCIE-0245 · Method and references | Specification and member examples | Not assessed |
| Observable cohorts | Immature horizons distinguished from zeroCIE-0246 · Method and references | Maturity mask and cutoff | Not assessed |
| Observable cohorts | Counts displayed alongside ratesCIE-0247 · Method and references | Numerator, denominator and period per cohort | Not assessed |
| Observable cohorts | Identity and collection breaks documentedCIE-0248 · Method and references | Change log and cross-device limitations | Not assessed |
| Influence evidence | Brief and criteria set before publicationCIE-0249 · Method and references | Objective, audience and measurement period | Not assessed |
| Influence evidence | Commercial intent checked on actual contentCIE-0250 · Method and references | Readable evidence of disclosure and advertiser | Not assessed |
| Influence evidence | Deliverables and reuse rights recordedCIE-0251 · Method and references | Published URL, approved version and usage scope | Not assessed |
| Influence evidence | Attribution separated from causal effectCIE-0252 · Method and references | Method, exclusions and evidence-limited conclusion | Not assessed |
| Project acceptance | Criteria connected to user tasksCIE-0253 · Method and references | Need, expectation and end-to-end scenario | Not assessed |
| Project acceptance | Outcomes separated from unexecuted trialsCIE-0254 · Method and references | Passed, failed and untested with reasons | Not assessed |
| Project acceptance | Exceptions explicitly decidedCIE-0255 · Method and references | Impact, owner, reason and deadline | Not assessed |
| Project acceptance | Handover and recovery included in acceptanceCIE-0256 · Method and references | Documentation and a task replayed by support | Not assessed |
| Inventory reservations | Physical and sellable states distinguishedCIE-0257 · Method and references | Dictionary and example per location | Not assessed |
| Inventory reservations | Reservation and release definedCIE-0258 · Method and references | Payment, cancellation and return transitions | Not assessed |
| Inventory reservations | Last unit tested concurrentlyCIE-0259 · Method and references | Two requests and one verified business allocation | Not assessed |
| Inventory reservations | Channel inventories reconciledCIE-0260 · Method and references | Movements, delays and justified corrections | Not assessed |
| HTTP caching | HTTP and application layers inventoriedCIE-0261 · Method and references | Caches and policy for each response | Not assessed |
| HTTP caching | Cache directives used according to their meaningCIE-0262 · Method and references | no-cache, private and no-store checked on responses | Not assessed |
| HTTP caching | Two-account isolation exercisedCIE-0263 · Method and references | Fictional markers at shared URIs and warm caches | Not assessed |
| HTTP caching | Invalidation after access changes testedCIE-0264 · Method and references | Revocation and absence of stale exposed content | Not assessed |
| JSON-LD acceptance | Properties connected to visible contentCIE-0265 · Method and references | Markup-to-page-evidence correspondence | Not assessed |
| JSON-LD acceptance | Syntax, vocabulary and feature support distinguishedCIE-0266 · Method and references | Validation results and eligibility limits | Not assessed |
| JSON-LD acceptance | Dates, prices and authors consistentCIE-0267 · Method and references | Common source and representation comparison | Not assessed |
| JSON-LD acceptance | Support reviewed after documentation changesCIE-0268 · Method and references | Dated register without rich-result promises | Not assessed |
| Accessible video | Audio and visual needs planned in the scriptCIE-0269 · Method and references | Information inventory and necessary alternatives | Not assessed |
| Accessible video | Captions reviewed and synchronizedCIE-0270 · Method and references | Names, numbers, useful sounds and speakers checked | Not assessed |
| Accessible video | Crops and languages checked after editingCIE-0271 · Method and references | Small-screen acceptance and reviewed translation | Not assessed |
| Accessible video | Accessible alternative available on publicationCIE-0272 · Method and references | Working link and comprehension without an imposed modality | Not assessed |
| Motion and pause | Motion inventoried by triggerCIE-0273 · Method and references | CSS, scripts, scrolling and media recorded | Not assessed |
| Motion and pause | Reduced-motion preference exercisedCIE-0274 · Method and references | Loading and live preference changes tested | Not assessed |
| Motion and pause | Pause and interaction criteria distinguishedCIE-0275 · Method and references | WCAG 2.2.2 and 2.3.3 conditions documented | Not assessed |
| Motion and pause | Final state reliable without animationCIE-0276 · Method and references | Task, progress and error feedback verified | Not assessed |
| Structured extraction | Shape and factual fidelity checked separatelyCIE-0277 · Method and references | Versioned schema, source passages and business rejections tested | Not assessed |
| Time and cutoffs | Periods and late events reconciledCIE-0278 · Method and references | Time zone, boundaries, cutoff and revisions documented | Not assessed |
| Email preferences | Opt-out enforced through sendingCIE-0279 · Method and references | Unsubscribe tested across imports, segments and queued campaigns | Not assessed |
| Architecture decisions | Choices and review triggers traceableCIE-0280 · Method and references | Options, constraints, consequences and review triggers retained | Not assessed |
| Review provenance | Origin, moderation and rating consistentCIE-0281 · Method and references | Dates, rejection reasons and visible aggregates reconciled | Not assessed |
| API pagination | Complete reading and recovery exercisedCIE-0282 · Method and references | Ordering, continuation, permissions and exported identifiers checked | Not assessed |
| Web pagination | Final pages reachable through linksCIE-0283 · Method and references | Distinct URLs, canonical URLs and script-free journeys tested | Not assessed |
| Social indicators | Comparisons use stable definitionsCIE-0284 · Method and references | Units, denominators, populations and periods displayed | Not assessed |
| Status messages | Action outcomes perceptible without losing contextCIE-0285 · Method and references | Announcement, focus, persistence and recovery tested with assistance | Not assessed |
| Shared caching: test privacy, variants and invalidation | Inspect effective rules · Test separation between users · Exercise version correctionCIE-0286 · Method and references | Response captures for two fictional accounts, signed-out state and purge after a change | Not assessed |
| URL migration: prepare mappings and test redirects | Choose relevant destinations · Test responses and signals · Check journeys after switchingCIE-0287 · Method and references | Old URL, final target, language, HTTP status and journey result mapping | Not assessed |
| Progressive releases: stop criteria and rollback | Build a useful comparison · Set expansion conditions · Exercise complete recoveryCIE-0288 · Method and references | Test record with population, stop criteria, recovered version and persistent effects | Not assessed |
| OCR: validate document reading before automation | Meaning and source defined — Check omissions, numbers and reading order before transcription feeds search or decisions.CIE-0289 · Method and references | Identified source, version, scope and owner | Not assessed |
| OCR: validate document reading before automation | Acceptance executed — Build a readable reference · Test consequential errors · Check structureCIE-0290 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| OCR: validate document reading before automation | Boundary and handling explicit — No. Check fields whose errors change the outcome; an overall score can conceal an amount error.CIE-0291 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Missing data: distinguish absence, zero and estimation | Meaning and source defined — Prevent silent replacement of absent values from changing the meaning of metrics.CIE-0292 · Method and references | Identified source, version, scope and owner | Not assessed |
| Missing data: distinguish absence, zero and estimation | Acceptance executed — Check the denominator · Compare coverage · Document estimationCIE-0293 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Missing data: distinguish absence, zero and estimation | Boundary and handling explicit — Only when the business definition establishes that absence actually means zero. Otherwise the result changes meaning.CIE-0294 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Campaign QR codes: verify the printed material and destination | Meaning and source defined — Test the path from print to digital service, including redirects and campaign retirement.CIE-0295 · Method and references | Identified source, version, scope and owner | Not assessed |
| Campaign QR codes: verify the printed material and destination | Acceptance executed — Test final printing · Inspect the journey · Inspect circulated materialCIE-0296 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Campaign QR codes: verify the printed material and destination | Boundary and handling explicit — Readability does not validate the destination. Compare domain and action with the material register.CIE-0297 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Retiring a digital service: remaining needs, data and handover | Meaning and source defined — Organise closure without abandoning ongoing cases, users or retention responsibilities.CIE-0298 · Method and references | Identified source, version, scope and owner | Not assessed |
| Retiring a digital service: remaining needs, data and handover | Acceptance executed — Resolve open cases · Prepare data · Inform and test handoversCIE-0299 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Retiring a digital service: remaining needs, data and handover | Boundary and handling explicit — No. Processing, integrations, data or requests can remain active. Verify these dependencies separately.CIE-0300 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Subscriptions: connect cancellation, billing and access rights | Meaning and source defined — Verify what changes after a stop request, immediately or at a planned period boundary.CIE-0301 · Method and references | Identified source, version, scope and owner | Not assessed |
| Subscriptions: connect cancellation, billing and access rights | Acceptance executed — Connect systems · Test period boundaries · Confirm clearlyCIE-0302 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Subscriptions: connect cancellation, billing and access rights | Boundary and handling explicit — Not automatically. Effects depend on contract, applicable rules and selected processing; verify states separately.CIE-0303 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Asynchronous API jobs: track status, resume and cancel | Meaning and source defined — Separate accepted requests, started processing and final outcomes of long-running operations.CIE-0304 · Method and references | Identified source, version, scope and owner | Not assessed |
| Asynchronous API jobs: track status, resume and cancel | Acceptance executed — Protect tracking · Bound status queries · Test concurrent cancellationCIE-0305 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Asynchronous API jobs: track status, resume and cancel | Boundary and handling explicit — No. Processing is not necessarily complete. The client needs access to an authoritative outcome.CIE-0306 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Sitemaps: verify URLs, shards and lastmod dates | Meaning and source defined — Check the file offered to crawlers beyond simple XML syntax validity.CIE-0307 · Method and references | Identified source, version, scope and owner | Not assessed |
| Sitemaps: verify URLs, shards and lastmod dates | Acceptance executed — Check contents and responses · Prepare partitioning · Make lastmod meaningfulCIE-0308 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Sitemaps: verify URLs, shards and lastmod dates | Boundary and handling explicit — No. It helps discovery. Availability, directives and content quality remain separate.CIE-0309 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Community polls: interpret who responds and who is missing | Meaning and source defined — Use answers as a documented signal without automatically treating them as the opinion of an entire audience.CIE-0310 · Method and references | Identified source, version, scope and owner | Not assessed |
| Community polls: interpret who responds and who is missing | Acceptance executed — Test the question · Document recruitment · Publish countsCIE-0311 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Community polls: interpret who responds and who is missing | Boundary and handling explicit — Volume alone does not correct participant selection. Examine who could see the question and who chose to answer.CIE-0312 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
| Localized input: resolve number and date ambiguity | Meaning and source defined — Accept and confirm values without silently changing separators, units or date order.CIE-0313 · Method and references | Identified source, version, scope and owner | Not assessed |
| Localized input: resolve number and date ambiguity | Acceptance executed — Retain raw input · Confirm the interpreted value · Test interactionsCIE-0314 · Method and references | Inputs, expected result, observed result and correction | Not assessed |
| Localized input: resolve number and date ambiguity | Boundary and handling explicit — It formats values. Define and test parsing rules for your field separately.CIE-0315 · Method and references | Rejected or ambiguous cases, decision and recovery owner | Not assessed |
No controls match these filters.
How to use the matrix
- 01
Score facts
Assign a level from observable evidence, not an intention or a purchased tool.
- 02
Connect to risk
Prioritise controls that protect a critical asset, sensitive decision or important customer journey.
- 03
Name an owner
Give every action an owner, due date and simple validation criterion.
- 04
Run it again
Retain evidence and reassess after major change, an incident or at least annually.
Illustrative example
Turn a control into a verifiable decision
Suppose an ordering service depends on an email provider. Use the matrix to examine this particular service: its importance, available evidence and the action to test. The levels below illustrate a method, not an assessment of any organisation.
Set the scope
Order confirmation, sender identity, supplier agreement and fallback channel each have a separate owner and business effect.
Score with evidence
A written recovery procedure that has never been tried is not a managed control. Keep the date, result, failure and fix from the latest test.
Make the decision
If an outage blocks an obligation to the customer, prioritise a fallback channel and set a switchover test. Record the owner and review date.
Do not turn summed scores into a universal label. The same level can hide different impacts depending on assets, affected people and dependencies; keep that context beside the score.