Resources · 02
Cyber exposure assessment: a prioritised checklist
Inventory what is visible, connect exposure to business assets and turn findings into a verifiable risk-reduction plan.
· 2 min
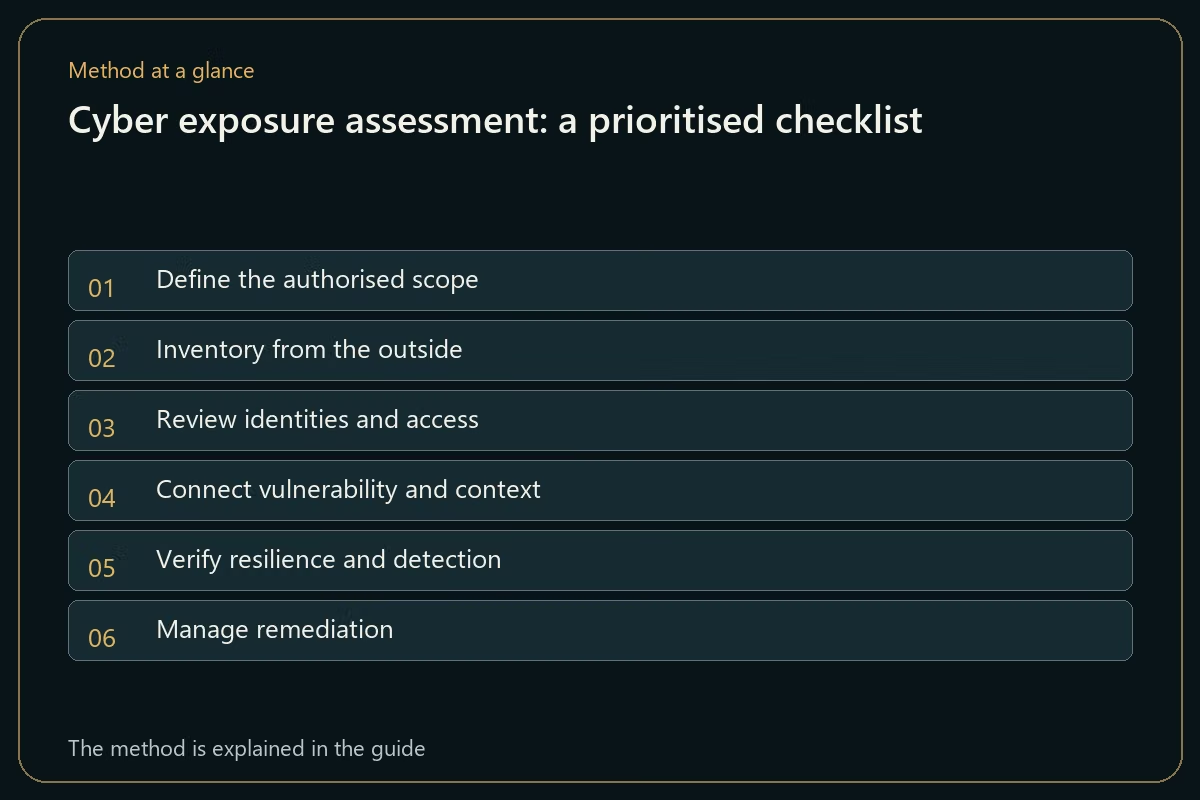
What this guide helps achieve
- Find forgotten assets
- Separate exposure from actual risk
- Address credible attack paths first
- Prove that a finding is closed
Quick check
- Does every domain have an owner?
- Do administrators use phishing-resistant MFA?
- Are test services exposed?
- Has restoration been tested?
- Does every exception expire?
Step-by-step method
- 01
Define the authorised scope
List entities, domains, ranges, cloud applications and exclusions. Agree allowed techniques, timing and an emergency contact.
Deliverable: scope and rules of engagement.
- 02
Inventory from the outside
Correlate DNS, certificates, published services, visible technology, public repositories and official accounts. Assign every asset an owner.
Deliverable: dated inventory.
- 03
Review identities and access
Check MFA coverage, orphan accounts, standing privileges, recovery mechanisms and exposed secrets.
Deliverable: critical access map.
- 04
Connect vulnerability and context
A weakness becomes a priority when it is reachable, exploitable, linked to critical data or function and insufficiently detected.
Deliverable: risk scenarios.
- 05
Verify resilience and detection
Review backups, restoration, logging, alerts, dependencies and crisis procedure. An untested backup remains an assumption.
Deliverable: test evidence.
- 06
Manage remediation
Give each action an owner, date, expected evidence and residual risk. Revalidate externally after the fix.
Deliverable: prioritised backlog.
Your acceptance workbook
Record observations against this guide’s criteria. A record is not certification.
The workbook does not save automatically. Export before leaving.
Filters do not limit exports. Actions include issues and unreviewed criteria.
Import replaces current observations after your confirmation.
Worked example
Illustrative situation
A subsidiary finds an old subdomain in search results. Before scanning, it confirms ownership, hosting, purpose and whether real data may still be present.
Decision and expected evidence
The exposure record separates an approved asset, an abandoned service and an unknown third party, with an owner and closure evidence for each.
Management indicators
| Indicator | What it measures | First action |
|---|---|---|
| Inventory coverage | Observed assets with an owner and criticality | Address ownerless assets first |
| Critical exposure | Sensitive services accessible from the Internet | Reduce access, segment or add strong controls |
| Time to remediate | Time from validated finding to closure evidence | Unblock high-impact, low-effort actions |
| Residual risk | Accepted exposure with an owner and expiry | Expire exceptions instead of leaving them open |
Common pitfalls
- Scanning without authorisation or a defined window
- Ranking only by a technical score
- Ignoring SaaS and historic subdomains
- Closing an action without confirmation testing
Frequently asked questions
Is an exposure review a penetration test?
No. It maps and qualifies visible exposure using non-intrusive or explicitly authorised methods. Penetration testing validates selected scenarios under a separate scope.
How often should the inventory be repeated?
After major change and regularly. External assets change quickly, so frequency should follow your deployment cadence.
Why test backups?
A file or successful job does not prove integrity or the ability to restore a service within the expected time.
Official references
Continue exploring
Related analysis