Resources · 06
Secure, high-performance web: a journey-led audit guide
Audit speed, accessibility, security and conversion around the actions users genuinely need to complete.
· 3 min
What this guide helps achieve
- Prioritise real user blockers
- Reduce weight, dependencies and attack surface
- Connect performance to conversion
- Validate fixes under realistic conditions
Quick check
- Are the three most valuable journeys named?
- Is field data segmented for mobile?
- Can the site be used by keyboard?
- Does every third-party script have an owner?
- Do form errors help users finish the action?
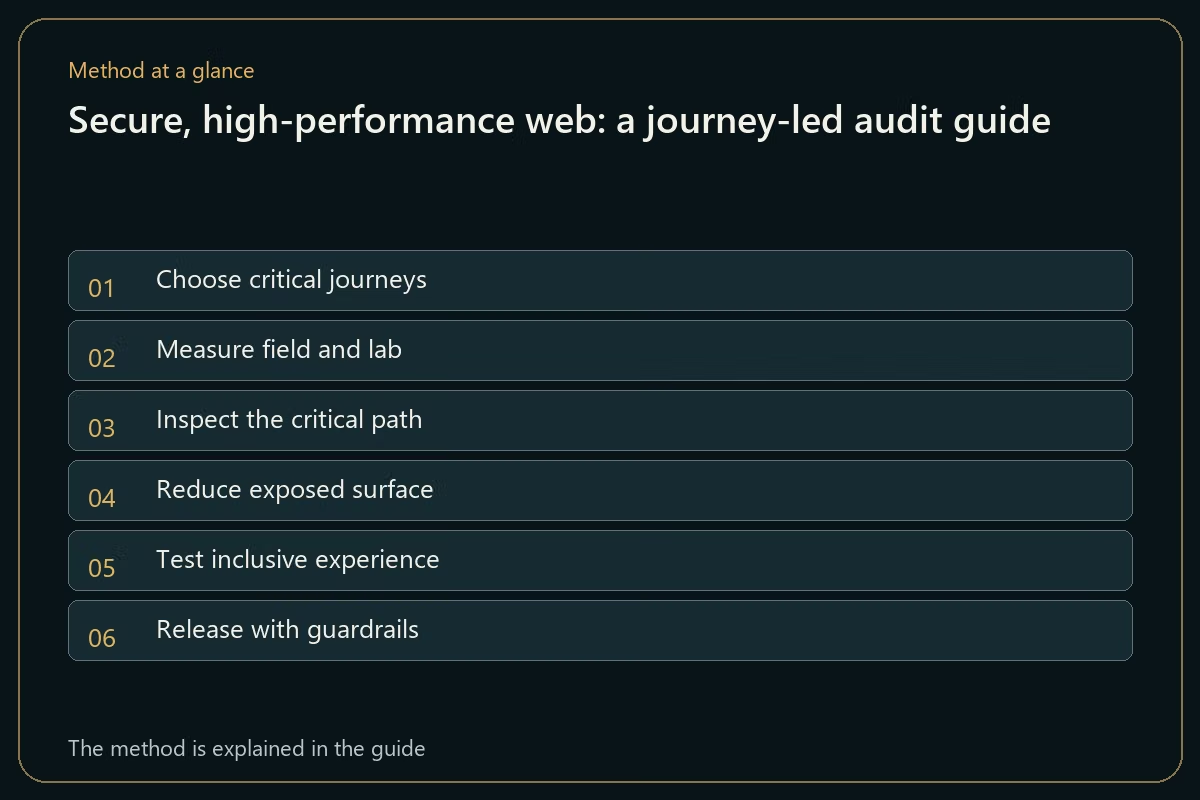
Step-by-step method
- 01
Choose critical journeys
Select search, reading, contact, signup, purchase or administration based on business value. Describe device, network, context and expected outcome.
Deliverable: prioritised test scenarios.
- 02
Measure field and lab
Combine aggregated real-user data with reproducible tests. Observe loading, responsiveness, stability, errors and abandonment without reducing analysis to one score.
Deliverable: segmented baseline.
- 03
Inspect the critical path
Review initial HTML, fonts, images, JavaScript, caching, server response and blocking resources. Give elements serving the journey an explicit budget.
Deliverable: performance budget.
- 04
Reduce exposed surface
Inventory third-party scripts, dependencies, headers, cookies, sessions, forms and admin interfaces. Remove the unnecessary and harden on the server.
Deliverable: dependency and protection register.
- 05
Test inclusive experience
Run every action by keyboard, screen reader, small screen, zoom and error state. Check labels, focus, contrast and recovery messages.
Deliverable: accessibility and friction report.
- 06
Release with guardrails
Automate stable controls, observe business outcomes after release and prepare rollback. A fix closes when the real journey improves without regression.
Deliverable: continuous validation plan.
Your acceptance workbook
Record observations against this guide’s criteria. A record is not certification.
The workbook does not save automatically. Export before leaving.
Filters do not limit exports. Actions include issues and unreviewed criteria.
Import replaces current observations after your confirmation.
Worked example
Illustrative situation
A booking page seems fast in a lab but its confirmation button responds slowly on mobile. The team segments field measurements by device and journey, then tests less JavaScript and keyboard behaviour.
Decision and expected evidence
The change is accepted only if the task remains accessible, interaction improves and the journey’s security controls still work.
Management indicators
| Indicator | What it measures | First action |
|---|---|---|
| Journey success | Users completing the action without a blocking error | Fix breaks shared by several segments first |
| Field performance | Loading, interaction and stability on real devices | Segment before targeting the dominant bottleneck |
| Third-party cost | Bytes, main-thread time and requests outside direct control | Remove, defer or replace each non-essential third party |
| Error rate | Technical and input failures by step | Improve prevention, message and recovery |
Common pitfalls
- Optimising the home page only
- Confusing a lab score with real experience
- Adding a security tool without removing unnecessary risk
- Damaging accessibility or measurement to save milliseconds
Frequently asked questions
Do performance and security conflict?
No. Reducing dependencies, JavaScript and unnecessary requests often improves both. Trade-offs should be measured against actual journeys and risk.
What score should we target?
One threshold does not replace field data. Set budgets by journey, device and audience, then track them alongside business outcomes.
Why include accessibility in the audit?
Because a fast action that cannot be used by keyboard, understood or recovered from remains a user and commercial failure.
Official references
Continue exploring
Related analysis